The PHP bug marks a harmful new period for the web. OpenAI’s poised to money in
Welcome to Eye on AI. Emily Forlini right here, filling in for Beatrice Nolan. In as we speak’s concern:
- Researchers discover a safety flaw affecting 70% of the online
- Anthropic might file for IPO as quickly as tomorrow
- Anthropic unveils Duet, its rival to OpenAI’s Dots and Meta’s Muse
- AI-driven layoffs at Barclay’s
I’ve been overlaying the rising variety of AI-powered hacks for months now, going again to when OpenAI’s fashions autonomously attacked Hugging Face in July. Ever since then there’s been a gentle drumbeat of incidents, and this month the tempo of alarming cyber information picked up significantly.
There have been more than 20 cybersecurity incidents in October, many simply this week. The web could formally be getting into a brand new period, one through which websites are inherently much less secure than they was. Cybersecurity paranoia is changing into desk stakes for anybody who goals to conduct commerce on-line. Some are saying that the brand new “moat” for companies is changing into how properly they’ll defend their prospects and IP from from AI-powered cyberattacks—not essentially what that IP or buyer base really is.
Security professionals have lengthy been warning that more and more highly effective AI instruments would empower dangerous actors to take advantage of bugs in code. This week, specialists told me, these warnings are actually coming true. AI fashions have change into noticeably extra highly effective at cyber duties in latest months. Specifically, they’re higher at processing massive quantities of code, and appearing autonomously. Hackers are having higher success setting off AI brokers on evil missions. Sometimes, many AIs work collectively in teams often called agent swarms. These swarms transfer faster than a human might sustain with.
So what’s a corporation to do within the face of those threats? The solely reply is to battle again with AI, that means to proactively “hack” your individual code, discovering bugs earlier than dangerous actors do after which patching them earlier than AI-armed hackers can strike. That’s precisely what occurred this week in an incident that has already change into the poster youngster for the approaching wave of AI-powered assaults. The incident concerned a legacy programming language referred to as PHP.
The PHP flaw heard ’around the global community
In August, a number of analysis groups at completely different organizations, all of them utilizing AI fashions to assist them hunt for safety flaws, discovered two vulnerabilities in PHP, which an estimated 70% of the online runs on. Those two bugs, in addition to the tactic for exploiting them, are actually collectively named “php2shell.” OpenAI’s GPT-5.6 Sol mannequin appears to have performed a key position on this discovery, though different fashions, together with Google’s Gemini 4 Argon, appear additionally to have performed a component.
The researchers handled the invention as an emergency, however the public didn’t discover out about it till this week, when on Oct. 20 the PHP basis introduced it will be issuing a essential patch inside the subsequent 24 hours. The following day, a coalition of corporations—together with OpenAI, Wiz, Calif, and extra—that had been privately engaged on a repair formally disclosed it. For the complete story on who first found the bug, and the way the businesses labored collectively over the previous two months, try the article I wrote on this earlier this week.
This could be a purely excellent news story a couple of potential disaster efficiently averted aside from a couple of inconvenient info. One is that information of the vulnerabilities and find out how to exploit them appears to have leaked within the days main as much as PHP’s announcement. According to Amazon Web Services, hackers began exploiting php2shell on Oct. 17, previous to the general public disclosure. It’s attainable they knew in regards to the bug, which a number of organizations, together with Amazon, had been notified about prematurely. They had all agreed to a particular time—14:00 UTC on Oct. 21—once they might put up about it as to not tip off the hackers early.
The different drawback was the day-long window between PHP asserting that it was about to concern a patch and when it really issued the patch, mixed with the time lag that it naturally takes many corporations to replace their programs after the patch was issued. After the general public disclosure of the exploit, the floodgates opened, and as of this writing there have been “tens of millions” of makes an attempt to take advantage of the bugs, whereas web sites across the global community constructed on flawed PHP code scramble to implement the patch. That work remains to be happening now. Luckily, the service most affected by the bug, WordPress, reports no points. (Separately, Fortune printed a great story this week on a failed coup of WordPress’s founder that’s value a learn.) Still, many governments and a few non-public entities determined to take some net providers offline to guard them from potential assaults whereas ready for the patch to be applied. This did save these websites from harm, but it surely additionally disadvantaged folks of the flexibility to make use of these providers.
Turning hacks into money
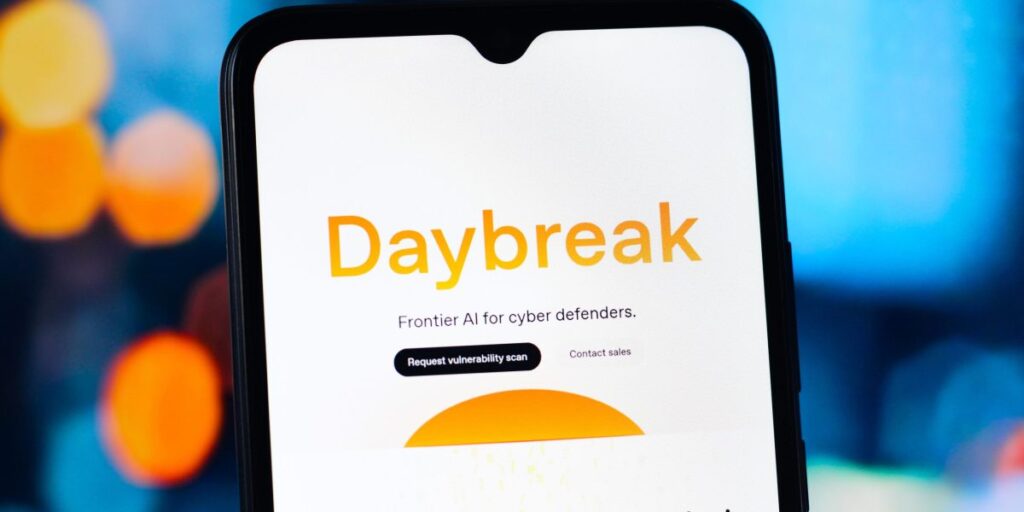
For organizations promoting defensive AI cybersecurity instruments, that is all excellent information. That consists of OpenAI. The firm has been constructing out its Daybreak program, which is an application-only initiative that grants organizations entry to its most refined instruments to assist defend towards refined, AI-powered assaults.
The program is rising quickly. Two weeks in the past, OpenAI up to date the Daybreak web site with new numbers. The variety of software program flaws its contributors have discovered swelled from 858 to 1,885. The variety of patches produced went from 263 to 661. The extra corporations and cybersecurity professionals enroll, the extra persons are utilizing OpenAI’s instruments to proactively discover and patch bugs of their code.
The PHP concern has raised additional consciousness of this program. OpenAI cofounder and president Greg Brockman gave it a lift too with an X post in regards to the PHP exploit and OpenAI’s position in discovering it—a uncommon, prolonged put up he has now pinned to the highest of his profile. Brockman additionally hired a brand new chief income officer over the summer time with a cybersecurity background, and tasked him with constructing out a gross sales group that may pitch its defensive software program to corporations.
OpenAI can also be planning to debut a brand new cybersecurity-focused mannequin this fall, in addition to a first-of-its type device to assist companies deploy it extra simply throughout their utilities. The firm appears to have made a proactive wager on AI-powered cybersecurity instruments being a burgeoning supply of income, and that prediction is coming true. And they’re removed from the one ones on this commerce; Anthropic has the same program for cybersecurity professionals at vetted organizations referred to as Project Glasswing, and a number of different SaaS suppliers provide AI-powered cyber protection instruments.
They could possibly be some critical money if the development continues—and so long as the hackers don’t get to them first.
With that, right here’s extra AI information.
Emily Forlini
[email protected]
@emilyforlini
FORTUNE ON AI
AI tools discovered the PHP vulnerability that could take down 70% of the internet. Now, the race is on to patch it before AI-powered hackers attack—by Emily Forlini
Exclusive: AI code-testing startup Blacksmith hits $1 billion valuation as AI-written code surges—by Beatrice Nolan
Anthropic adds Harvard astrophysicist to the trust that controls its board—by Jeremy Kahn
Powerful new AI models are fueling a growing wave of cyberattacks, experts say—by Emily Forlini
AI IN THE NEWS
Anthropic might make its IPO prospectus public as quickly as tomorrow. The public could lastly get solutions to many excellent questions on Anthropic’s commerce and its funds when the corporate makes public the prospectus for its deliberate IPO, a transfer that would come as quickly as tomorrow, in response to three folks acquainted the corporate’s plans who spoke to Yahoo! Finance. Anthropic’s public inventory providing could possibly be the biggest in historical past, valuing the Claude maker at greater than $2 trillion.
Anthropic unveils its Duet private agent. It’s the corporate’s reply to non-public assistant AI brokers reminiscent of Instinct, Meta’s Muse, and OpenAI’s Dots, but it surely’s solely out there now as a preview. Read extra here from Engadget.
Microsoft discloses ‘a whole lot’ of autonomous AI-powered hack by China state-aligned actor. The hacking group, often called Storm-0940, used an open-source AI platform referred to as Artex, developed in China. That’s the identical know-how behind a hack of South Korean banks earlier this month. Read extra here on the Microsoft weblog.
Barclays to chop 5,000 jobs in AI-driven push to decrease prices. The layoffs will have an effect on 5% of the corporate’s workforce, and are available after reporting a 12% enhance in quarterly revenue, falling in need of analyst forecasts. Is AI the savior to assist the corporate do extra with fewer workers? Read extra here within the New York Times.
EYE ON AI NUMBERS
10%
That’s how a lot of the inner site visitors to OpenAI’s Codex coding device went unmonitored for months this spring as a consequence of gaps in OpenAI’s inner security and monitoring procedures, in response to AI security companies Redwood Research and METR. The companies had been embedded at OpenAI for 3 weeks from July 21 to Aug. 11, throughout which they carried out an impartial audit of OpenAI’s safety posture. They discovered that from May to July OpenAI’s Codex agent site visitors was unmonitored, making a “protection hole that brokers might have exploited to misbehave with out being caught.” These are the identical months main as much as and through the Hugging Face cyber incident, though the report doesn’t say the dearth of monitoring performed a task in that case. METR and Redwood additionally discovered quite a few different gaps in OpenAI’s monitoring programs.
AI CALENDAR
Nov. 9-12: Web Summit, Lisbon, Portugal.
Nov. 16-17: Fortune 500 Innovation Forum, Detroit. Apply here to attend.
Nov. 18-19: Slush, Helsinki, Finland.
Dec. 6-12: Neural Information Processing Systems (Neurips) convention. Sydney, Australia.
Dec. 7-8: Fortune Brainstorm AI, San Francisco. Apply here to attend.