Reconstructing Machine Firmware From SPI Reads

If you wished to extract the firmware from a thriller system, you would possibly pull the flash chip out of it and toss it right into a reader. But in the event you solely had one probability to get it proper and couldn’t danger damaging the system within the course of, bodily eradicating the chip could seem a lot much less enticing. Reading the chip in-circuit failed — due to course it did — so what does that depart?
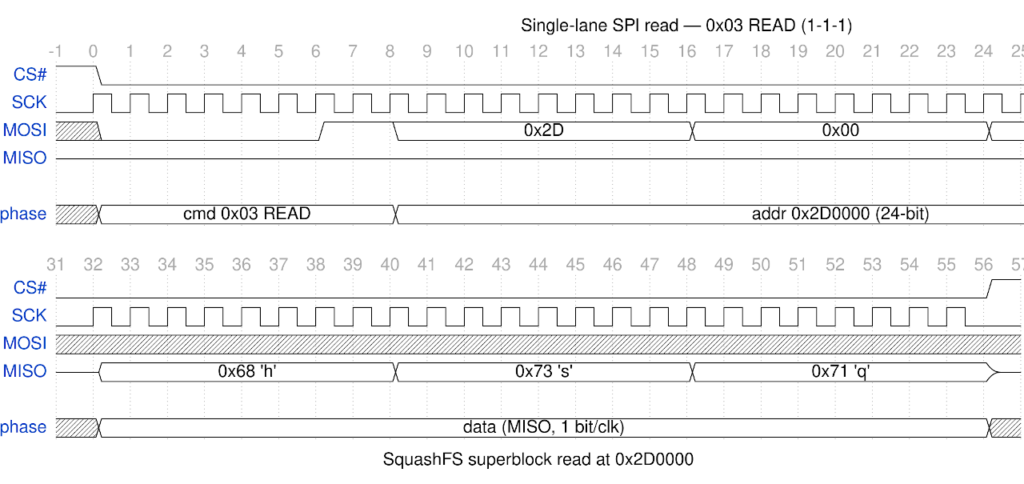
Well, in the event you observe the instance of [Matthew “wrongbaud” Alt], the following software you attain for could be a logic analyzer. In a recent write-up, [wrongbaud] explains the method of figuring out, capturing, and in the end decoding the SPI learn operations used to load the firmware from a standard W25Q-series flash chip at boot time. He notes it’s not an ideal resolution, as in the long run you’ll solely be capable to sniff out what the CPU truly reads, not essentially the whole contents of the chip, however it’s a giant step in the precise course in the event you’re reverse engineering one thing in the dead of night.
Before digging into the decoding of the captured information, [wrongbaud] does what he does finest and breaks down the nuts and bolts of SPI communication. Armed with the output from his logic analyzer and the datasheet for the flash chip, he explains how you can interpret the assorted alerts at play.
Even in the event you’re not terribly focused on slurping the firmware from thriller containers, it’s an important primer on how SPI works and an interesting learn for anybody who’s searching for a greater understanding of how chips speak to one another.
Once he’s lined the fundamentals and captured some information shifting throughout the SPI bus, [wrongbaud] strikes on to decoding it with Scapy. The highly effective Python software is mostly related to the manipulation of community packets, however as demonstrated right here, it may be turned free towards different varieties of information. With a bit of massaging, it will possibly work via the seize recordsdata produced by the logic analyzer and switch it into a picture file able to get loaded into binwalk.
But wait! Just while you suppose [wrongbaud] was achieved, he notes one thing a bit of odd — the firmware picture comprises the bootloader and Linux kernel, however there’s a giant hole the place the filesystem needs to be. It turns on the market’s a bit of extra work to be achieved, as earlier than the CPU hundreds the filesystem off of the chip, it kicks into the quicker Quad-SPI, which provides two extra information strains to the combination. That means extra capturing, a touch of additional processing, and a dd one-liner to merge the 2 picture recordsdata into one, however [wrongbaud] will get us there in the long run.
If that is the primary time you’ve run throughout [wrongbaud]’s work, you’re in for a deal with. From his overarching hardware hacking roadmap to deep dives into individual techniques such as fault injection, he’s produced phenomenal content material that’s nearly assured to show you one thing new.