I put in this free open-source app for Android to see what my apps had been truly connecting to

I exploit my PC loads, however truthfully, I exploit my cellphone much more. That’s the place I preserve my banking, chat, wallets, passwords, and mainly the accounts that matter to me. After Portmaster opened my eyes to all the background connections running on my PC that I hadn’t observed earlier than, I could not cease questioning what the apps on my cellphone had been doing that I did not learn about.
I did not need simply one other permissions display. I wished to see the connections themselves and see what my apps had been connecting to. That’s how I ended up with PCAPdroid.
I wished my cellphone to elucidate itself the best way Portmaster did
A firewall taught me the behavior earlier than seeing an app to make use of it with
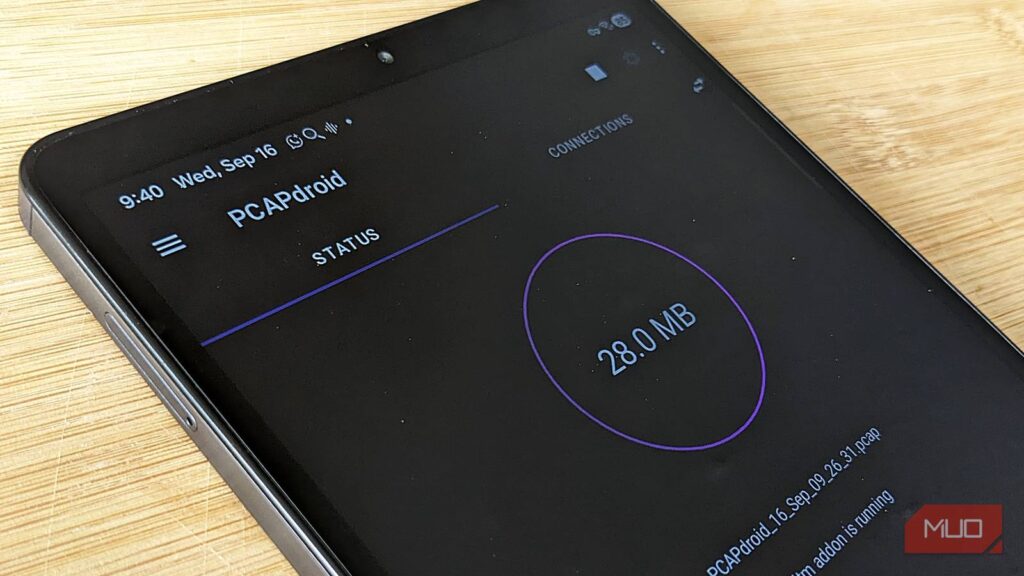
PCAPdroid was the closest factor I discovered to Portmaster for Android with out rooting my pill. It creates a neighborhood VPN and lets me see which app made a connection, the place it went, and the way a lot visitors was concerned. Once the seize session ended, I checked the Connections tab and exported the lists too, which made it a lot simpler to look by means of the domains.
I intentionally did not pay for any of the additional options. That’s as a result of what I wished was to see the background connections first, and the free model gave me that. Unlike Portmaster, it did not give me a lot context round a connection or flag something for me; It simply gave me data and left me to work out what I used to be .
I received HTTPS decryption working a bit. I put in the Mitm add-on and certificates as instructed, and a few the connections truly got here again marked “Decrypted.” That didn’t imply I may abruptly learn all the pieces, although.
Most connections confirmed certificates errors; some flat-out refused it as “Not decrypted,” and PCAPdroid advised me outright it couldn’t decrypt QUIC visitors in any respect, which covers quite a lot of what Google’s apps use. Even the decrypted connection nonetheless confirmed unreadable noise within the payload. That was sufficient to make me cease worrying about decrypting. The listing already gave me loads to take a look at.
My banking app had extra connections than I anticipated
OPay wasn’t simply speaking to its personal servers
OPay is my banking app, so I paid further consideration to each connection. It recorded 61 connections throughout 20 domains. Most had been its personal opayweb.com providers, together with connections for various elements of the app. Then I discovered AppsFlyer, datadoghq.com, app-measurement.com, graph.fb.com, and whatismyip.akamai.com.
That appeared like quite a lot of exterior sources speaking to my financial institution, so I regarded. I’d already encountered AppsFlyer earlier than, so I knew it’s used for attribution and measurement, extra like monitoring which apps are watching an installation and the place it got here from. Datadog is a monitoring and observability service, whereas app-measurement is related to Google’s analytics providers. Facebook and IP lookup are frequent for mobile money apps working advertising.
I didn’t discover something in these connections to imagine OPay was doing something shady. But I hadn’t identified any of it was there till I regarded, and that was the entire level for me.
Then a child’s recreation caught me off guard
Monster High was only a coincidence
While a seize session was working, my niece coincidentally picked up the pill to play Monster High. I didn’t assume a lot of it till I went by means of the log afterward.
PCAPdroid recorded 375 connections inside a couple of minutes. Among them had been a number of Pangle, AppLovin, DoubleClick, Moloco, Firebase Crashlytics, Chartboost, InMobi, TikTok-related advert domains, and visitors routed by means of Alibaba Cloud development projects.
That’s a heavier, extra aggressive advert and monitoring stack than a few of the apps I anticipated hassle from, and it is sitting inside a recreation a child was taking part in with none thought what was occurring beneath it.
WhatsApp Business, in distinction, recorded 121 connections over 2 hours, and almost all the pieces I checked led again to WhatsApp or Meta’s development projects.
My different apps did not take almost as a lot work
Except Chrome
Not each app goes on the lookout for firm. For occasion, Telegram barely registered something. SuperfreezZ, xnotes, Wispr Flow, Samsung Notes, Asana, Claude, Pluckeye, Slack, and different apps have minor footprints, however nothing odd.
Then I opened Chrome, and it modified the best way I learn the logs. It recorded 4,930 connections throughout 543 domains. That quantity regarded ridiculous, and my first response was that Chrome had quite a lot of explaining to do, till I began the place these connections had been going.
Plenty of them belonged to web sites I’d visited. From many of the domains I checked and researched, the connections led again to promoting, analytics, and third-party providers belonging to these web sites, on prime of no matter Chrome’s ad privacy feature already is aware of. Chrome was in the course of all of it, and the connection counts made the browser look accountable.
YouTube additionally confirmed me one thing comparable on a smaller scale. It had a number of domains with a number of megabytes, however the ones I checked traced again to Google’s downloader development projects.
That was in all probability the perk of going by means of the connections myself. A wierd-looking area did not keep unusual for very lengthy as soon as I knew who or what was behind it.
Running PCAPdroid wasn’t freed from issues
It got here with a number of unintended effects I did not count on

The longer I left PCAPdroid working, the much less snug I felt with leaving it working unattended. A few instances, a number of hours right into a seize session, my pill’s web connection would go unhealthy. Websites stopped loading, Spotify went offline, and YouTube and different apps would not load. While this occurred, the Wi-Fi labored wonderful on one other cellphone linked to the identical community.
Notifications additionally stopped arriving whereas a seize was working after which appeared as soon as I ended it. I noticed a few customers with comparable connectivity points within the app’s assessment part on the Play Store.
I additionally misplaced a number of seize classes as a result of I used to be utilizing the “No dump” mode, which saved the information in reminiscence. So, each time my freezer killed PCAPdroid in the background, the session was gone. I later switched to “PCAP file” mode to avoid wasting whereas working.
I’m nonetheless maintaining PCAPdroid put in, and it is was an precise behavior.
Checking an app’s connection is likely one of the first issues I do now at any time when I set up one thing new. I attain for PCAPdroid as a filter to see whether or not I’ll be snug giving an app each permission it requests.
Monster High caught with me, although. Everything else, together with OPay, Chrome, and the opposite apps I checked out, I understood and moved on. But I couldn’t perceive why a child’s recreation is that wired up with advert tech and monitoring providers.
So I put PCAPdroid on her mini-tablet too and went by means of what else was on there. I ultimately uninstalled Monster High from our tabs and eliminated a few others off hers as soon as I noticed the identical sample.
Being in a position to perceive what was occurring behind the scenes and use that to decide positively made all of the digging value it.