South Korea raises information breach fines to 10% of turnover

Companies behind main negligent information leaks can now face fines of as much as 10 p.c of annual turnover beneath revised privateness guidelines.
Korea’s privateness regulator is sharply elevating the price of information breaches, aiming to push corporations to deal with information safety as a preventive capital allocation relatively than a routine price of doing corporate affairs.
Starting Friday, corporations discovered to have leaked the private information of 10 million or extra individuals via intent or gross negligence might be fined as much as 10 p.c of their complete turnover as a part of a broader overhaul beneath the revised Personal Information Protection Act that’s set to take impact the identical day. Even if a leak hasn’t been confirmed, corporations should notify customers inside 72 hours if the chance of publicity is excessive.
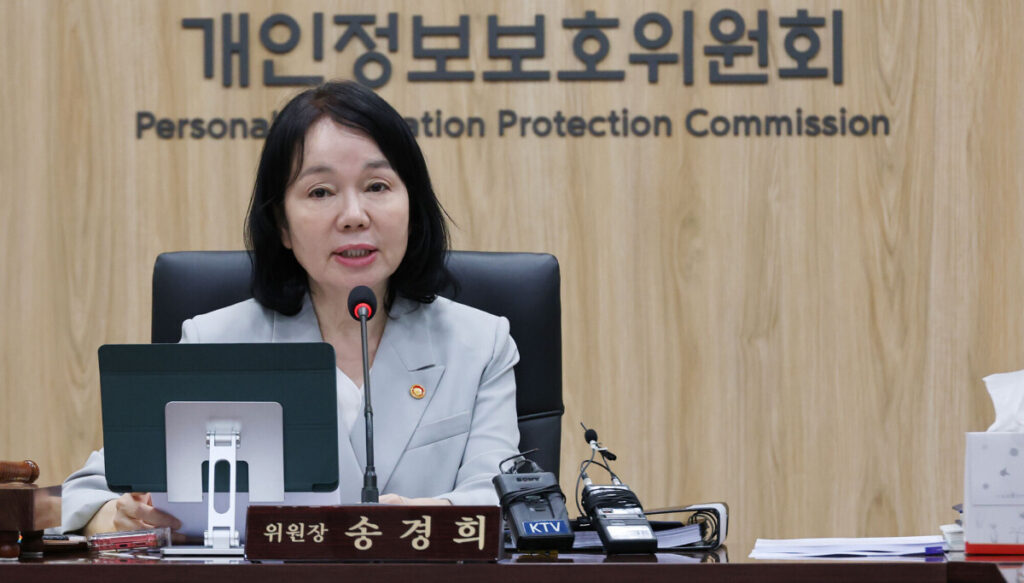
“Personal information breaches have lately occurred repeatedly and grown in scale in fields carefully tied to day by day life, resembling retail and telecommunications,” Personal Information Protection Commission (PIPC) Secretary General Yang Cheong-sam advised reporters Thursday. “We’ve improved the system to carry severe violations strictly accountable whereas additionally serving to forestall breaches from occurring within the first place.”
Under the enforcement decree, the cap applies to corporations that repeatedly commit intentional or grossly negligent violations inside three years, or that fail to adjust to a corrective order and go on to endure a breach in consequence. Fines are calculated primarily based on the character and severity of the violation, the circumstances concerned and the dimensions of the harm.
Before the revision, corporations had been topic to a penalty of as much as 3 p.c of gross sales.
The hole between the outdated and new guidelines turns into clear when utilized to an actual case. Local e-commerce big Coupang was fined 624.6 billion gained ($466.3 million) in June after leaking the private information of 37.55 million individuals. Applying the brand new commonplace to that case may push the high-quality into the trillions of gained. However, precise penalties will nonetheless rely on intent, negligence, the dimensions of harm and any mitigating components.
Companies that invested in information safety beforehand will get credit score beneath the brand new guidelines. Regulators will take into account the dimensions and continuity of an organization’s capital allocation in information safety budgets, staffing and tools, together with its broader safety system, together with its chief privateness officer, to cut back a high-quality by as much as 40 p.c. An organization that detects a breach early, experiences and notifies customers promptly, and prevents the harm from spreading may also obtain as much as a 40 p.c discount.
The revision additionally introduces a “potential information breach notification system.” If an organization determines there’s a excessive probability that non-public information was uncovered — as an illustration, after unlawful entry to its information processing programs, or after discovering that some private information was illegally traded in a method that implies others’ information might have leaked too — it should notify affected people inside 72 hours of studying that. Data cast, altered or broken by ransomware and comparable assaults is now additionally topic to the identical reporting and notification necessities.
The authority and accountability of chief privateness officers at main corporations and establishments may also increase. Companies with annual turnover exceeding 180 billion gained that course of the private information of 1 million or extra individuals, or the delicate or distinctive figuring out data of fifty,000 or extra individuals, should get board approval earlier than appointing, altering or dismissing a chief privateness officer and report the choice to the PIPC. Universities with 20,000 or extra college students, tertiary normal hospitals and operators of main public programs fall beneath the identical requirement.
“We count on the way in which corporations view capital allocation in information safety to shift from seeing it as a value to treating it as a proactive capital allocation that builds buyer belief and expands company revenue,” PIPC’s Chairperson Song Kyung-hee mentioned.
BY HAN EUN-HWA [[email protected]]