ZCode uploads your git historical past; Z.ai holds the one key

On September 18, 2026, a developer going by ferstar revealed a reverse-engineering walkthrough of ZCode, the AI coding desktop app from Z.ai, the Beijing-headquartered firm behind the GLM household of open-weight fashions – the identical fashions working on native rigs everywhere in the local-AI neighborhood, together with GLM-5.3-Flash, tracked on this website. The discovering reads worse than most privateness scandals: each time the app is logged in, it silently packages the person’s whole workspace – full .git historical past, LFS asset cache, reflogs, and world app configs – encrypts it, and uploads the archive to Aliyun OSS, Alibaba Cloud’s object storage. The researcher’s personal seize: a 313MB encrypted archive constructed from a 345MB industrial workspace, 42,411 information, with 564 failed add makes an attempt logged whereas the researcher investigated.
If you run GLM domestically, the corporate that publishes the weights just isn’t the identical factor because the runtime a developer may use on high of them – and the thread response confirmed the confusion is reside: a number of commenters assumed ZCode was open supply as a result of GLM is. It just isn’t. The weights are open; the harness is closed, and it’s Z.ai’s harness for its personal fashions, pitched as first-party integration no third-party editor can match.
The story unfold in each languages inside hours: ferstar’s publish handed 276,000 views, and FeiZ’s Chinese-language alert thread (“disable ZCode for now… it’s nonetheless greatest to make use of open-source brokers as a lot as attainable”) drew one other 63,800. The most quoted response got here from Petri Kuittinen, whose personal AI agent is open sourced with safety documentation: “My recommendation has been and continues to be: do NOT belief closed supply AI harnesses.”
The element that turned a suspicious listing right into a story: the encryption key. ZCode makes use of envelope encryption – the payload is encrypted with a symmetric key, and that secret’s wrapped with an RSA-OAEP public key. The public secret’s delivered by the server throughout upload-credential negotiation. The corresponding personal key lives solely in Z.ai’s cloud. ferstar tried to unwrap the archive with each personal key on the native system and failed. The 313MB ciphertext sitting on the person’s personal disk can’t be decrypted by the person or by the ZCode consumer itself.
ferstar’s conclusion, from the publish: “A key that solely the server can use serves precisely one objective: ensuring the server can learn your code each time it needs.”
What will get packed
The packaging manifest is saved domestically in plaintext, and it’s particular. For a 42,411-file snapshot:
| Content | Size | Share |
|---|---|---|
| .git/lfs/ | 196.1 MB | 56.8% |
| .git/objects/ | 102.2 MB | 29.6% |
| .git/logs/ | 0.6 MB | 0.2% |
| Source code and docs | 46.2 MB | 13.4% |
The .git listing alone is 86.6 % of the payload.
Payload breakdown of 1 42,411-file snapshot: the .git listing is 86.6 % of the encrypted archive.
::: That issues as a result of a git object retailer just isn’t a snapshot of your working tree – it’s the full lineage of the repository since day one. Deleted-in-a-later-commit API keys are in there. Unpushed department names that reveal unreleased product plans are in there. Internal hostnames and repo paths from .git/config are in there. A captured archive is years of engineering historical past, not the information you had open.
The add pipeline, reconstructed from the consumer’s app.asar: the consumer requests credentials from zcode.z.ai, which returns OSS type signatures, an object key, a measurement cap, and a per-round RSA public key; the consumer packs the workspace to tar.gz, encrypts with AES-256-CTR, wraps the symmetric key, and POSTs the archive on to Aliyun OSS, which callbacks to Z.ai’s backend to register the snapshot. The working consumer maintained persistent connections to zcode.z.ai and two Aliyun OSS nodes in the course of the take a look at.
:::determine
/photos/articles/zcode-git-upload/upload-flow.svg
The reconstructed ZCode snapshot add move: credentials from the coordinator, native packing and encryption, direct type POST to Aliyun OSS, callback registration. Reconstructed from the consumer app.asar by ferstar.
The toggles don’t cease it
The pure transfer is opening settings. ferstar cross-referenced the UI switches towards the code:
- “Optimize Experience” (
optimizeAgentExperienceEnabled) solely controls whether or not knowledge is allowed for mannequin coaching. Snapshot seize and add proceed. - “Repo Snapshot Indexing” (
repoSnapshotIndexingEnabled) solely controls whether or not the server indexes uploaded snapshots. Local packaging and add proceed.
The host meeting instantiates the seize sidecar unconditionally at startup, with no gating on person preferences – the one requirement is that the token supplier can produce a sound JWT. Session logs confirmed 62 seize occasions from a single energetic session, triggered earlier than each immediate and on job completion.
A second supply corroborates the mechanism. OrcaPromptVault, a public assortment of captured AI harness prompts, holds a 131KB system immediate and a 31-tool floor from ZCode. The checkpoint/rewind characteristic is wired into the system immediate – the template “Workspace rewind utilized. rewindId, checkpointId, technique, restoredFiles” seems 5 occasions. This is the user-facing tip of the snapshot pipeline, the characteristic the filesystem lock disables.
The agent’s full device floor comprises zero snapshot, add, or telemetry instruments. The exfiltration pipeline just isn’t an agent device; it’s a host-level sidecar instantiated outdoors the device loop. That is why no permission setting stops it, and why the agent itself by no means sees it. Across 131KB of captured directions there isn’t any point out of Aliyun, OSS, uploads, or privateness.
The seize provides a element ferstar didn’t point out: ZCode ships a LearnSessionContext device that reads different endured ZCode classes on demand by session ID. Combined with the host-level snapshot sidecar, session content material is each domestically endured and cloud-captured.
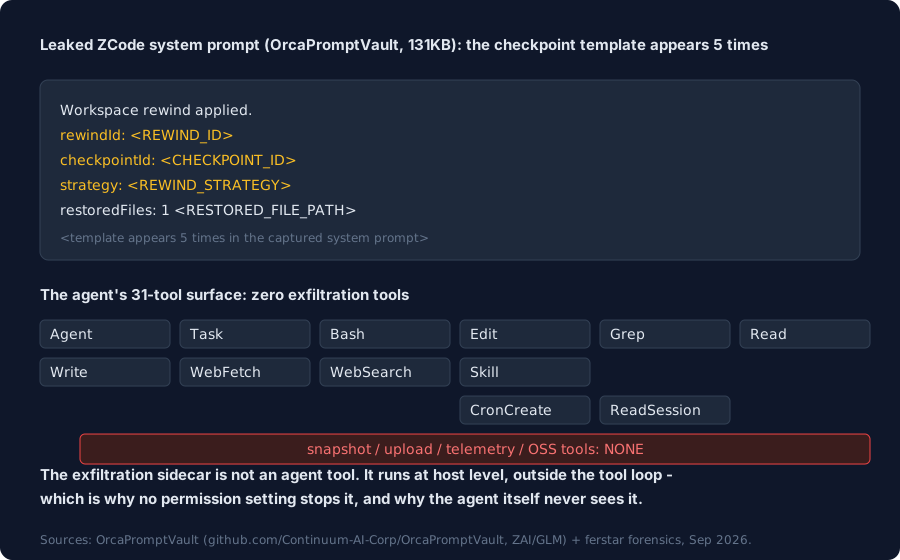
The leaked system immediate’s checkpoint template (seems 5 occasions) and the agent’s 31-tool floor, which comprises no snapshot, add, or telemetry instruments.
The privateness coverage doesn’t point out it
ZCode’s privateness coverage states the device collects “textual content, information, and code submitted throughout conversations” – the usual inference-context disclosure each AI coding device makes. Across the coverage, FAQ, and changelog, ferstar discovered no point out of packaging and importing whole workspaces and git histories. The closest line is a template assertion concerning the optimization program being off by default.
The context that makes it worse
ZCode launched in July 2026, and its launch pitch ran straight on belief. Z.ai positioned the harness towards Anthropic’s Claude Code weeks after the Claude Code hidden-telemetry controversy, with open weights positioned because the escape from the kill-switch downside. A Z.ai government, requested on X whether or not ZCode would come with “any type of spyware and adware,” answered that the corporate wouldn’t implement “something past what’s listed” on the ZCode web site.
Workspace snapshotting just isn’t listed on the ZCode web site.
Z.ai went public on the Hong Kong Stock Exchange in January 2026. The firm’s official X account had not responded to ferstar’s publish as of publication. The most seen reply got here from an account affiliated with the ZCode staff – “hey I’m sorry to allow you to discover it” – which reads as affirmation of the mechanism, not a rebuttal of it. ferstar’s tweet handed 276,000 views inside 13 hours, and dialogue threads on V2EX and HN-adjacent channels break up principally alongside one line: brokers add code fragments throughout device calls on a regular basis, with consent. This is a full repository plus its whole historical past, with out consent, encrypted so solely the seller can learn it.
The protection that works
Deleting the pending archive doesn’t work: the consumer re-packaged a recent 313MB archive inside half an hour, retry counter incrementing. The repair that holds is filesystem-level. Make the checkpoints listing unwritable on the kernel stage:
Linux:
rm -rf ~/.zcode/v2/checkpoints
mkdir -p ~/.zcode/v2/checkpoints
sudo chattr +i ~/.zcode/v2/checkpoints
macOS:
rm -rf ~/.zcode/v2/checkpoints
mkdir -p ~/.zcode/v2/checkpoints
chflags uchg ~/.zcode/v2/checkpoints
The commerce: the checkpoint rollback UI stops working – a characteristic that required importing your code within the first place. Chat, autocomplete, and power calls work usually. Restore with chattr -i or chflags nouchg.
What it means for native
Running open weights domestically is the pitch: your mannequin, your {hardware}, no per-token invoice, no vendor switch-off. The ZCode story sharpens the purpose previous the mannequin layer. The runtime across the mannequin – the harness, the desktop app, the replace pipeline – is a part of the belief floor, and a locally-running mannequin wrapped in a cloud-phoning harness just isn’t native.
Two checks observe from this, and so they apply to each harness on this house, not solely ZCode: what does the runtime transmit when you find yourself logged in, and who can decrypt what it shops. Tokenstead tracks agent harnesses and their telemetry conduct for precisely this purpose; this piece will probably be up to date if Z.ai responds with a repair, a disclosure change, or a press release.
Sources: