The CISA Alert: Security Past Solitary Confinement
Written by Bruce Cloutier on Aug 11, 2026 1:39 pm
Summary: CISA is correct to sound the alarm over Internet-exposed operational know-how. But should each undesirable connection be answered with extra authentication, stronger cryptography, and extra processing energy? There are remarkably light-weight methods to make malicious automation work tougher whereas permitting OT controllers to focus on the job they had been put in to do.
>> The Alert Is Worth Taking Seriously
CISA has issued an pressing warning in regards to the continued publicity of operational know-how (OT) to the general public Internet. The message is direct and intentionally uncompromising: act now. Remove OT connections to the general public Internet, change default passwords instantly, limit distant entry, and strengthen authentication and community protections. These aren’t introduced as recommendations for future consideration, however as fast steps wanted to scale back the rising cyber menace to industrial techniques. [1]
The urgency is justified. But the rising want for OT connectivity makes one advice significantly tough: merely eliminating the flexibility to speak just isn’t at all times an possibility. Nor ought to the choice be restricted to an escalating cycle of stronger cryptography, higher computational necessities, and eventual {hardware} substitute. There is one other class of protection that deserves much more consideration: strategies that cut back the attacker’s alternative whereas consuming nearly not one of the controller’s sources. Perhaps it’s time to carry a few of these to the desk and broaden the dialog.
Any IT skilled who has noticed the unfiltered community visitors at an Internet-facing system is aware of that the priority is completely justified. The public Internet is a very hostile setting. Within minutes, an uncovered system will encounter port scans, connection probes, login makes an attempt, protocol fingerprinting, credential assaults, and different automated exercise. Most folks by no means see any of this and are consequently unaware simply how relentless it’s.
JANOS, the working system on the coronary heart of the JNIOR, was purpose-built from the begin to help each OT and IT necessities. That has additionally made JANOS one thing of a proving floor. While the overwhelming majority of JNIORs function inside air-gapped or in any other case managed networks, we have now deliberately operated models immediately on public IP addresses – the worst-case publicity – to watch, perceive, and develop defenses towards this type of exercise. Watching that visitors in actual time rapidly adjustments one’s perspective on what an embedded system ought to be anticipated to tolerate.
Strong login credentials are a vital protection, however an attacker doesn’t must efficiently log in to create an issue. A sustained password assault can devour important processor sources for minutes at a time. Consider an SSH login assault the place each try requires the controller to barter a safe connection earlier than credentials may even be evaluated. As safety algorithms develop into stronger, the computational financial backing in every undesirable connection will increase. The attacker doesn’t must defeat the cryptography. It want solely make the controller carry out it. For an OT controller anticipated to take care of deterministic operation, merely processing the assault turns into a part of the menace. Whether intentional or not, the outcome can start to resemble a denial-of-service (DoS) assault towards the controller.
Have we been addressing the issue or amplifying it?
>> Not Every Attack Is Stuxnet
It is helpful to tell apart between focused assaults and the large quantity of indiscriminate malicious exercise continuously circulating on the Internet. Stuxnet is probably the traditional instance of a focused industrial assault. Its creators understood the techniques they supposed to compromise, developed subtle strategies particularly to succeed in them, and had a really specific goal. Most hostile Internet visitors is nothing like that.
An nearly fixed stage of ongoing assault is generated by automated techniques sweeping huge tackle ranges in search of listening ports, recognizable providers, weak software program, or credentials that simply occur to work. The intent may not be “search and destroy.” The objective could be nothing greater than to find a possible goal and add that to an inventory to be offered to the very best bidder. Those techniques usually do not know what tools they’ve discovered. Yet each response they provoke imposes some value on the tools whereas costing the scanner comparatively little.
That distinction issues. Defending towards a decided adversary with detailed information of your tools is a really completely different downside from coping with the relentless background exercise of the Internet. Yet each arrive on the similar community interface and demand consideration from the identical finite set of sources. In an OT system, these sources are accountable for monitoring inputs, controlling outputs, executing software logic, and sustaining deterministic operation. There is little profit in permitting nameless automated scanners to compete for them.
The apparent response is to forestall as a lot pointless visitors as doable from distracting the controller. In an IT globe of routers, firewalls, proxies, and managed switches, does the OT skilled actually know whether or not their edge controllers are in danger?
>> What Does “Internet-Facing” Mean?
An Internet-facing OT system doesn’t essentially have its personal public IP tackle. The most blatant—and most uncovered—case is a controller assigned a public IP tackle and linked on to the Internet. More generally, the controller resides on a non-public community behind a router or firewall utilizing Network Address Translation (NAT), the place unsolicited Internet visitors usually can’t attain it. That adjustments when port forwarding is configured. A router could be instructed, for instance, to ahead incoming SSH or internet connections to a particular controller on the non-public community. The controller nonetheless has a non-public IP tackle, however a number of of its providers are actually successfully uncovered to the general public Internet. From the attitude of an automatic scanner, there could also be little sensible distinction. It discovered a port, despatched a request, and one thing answered.
Not all exterior connectivity creates that very same publicity. A controller that initiates an outbound connection by NAT doesn’t mechanically develop into accessible for unsolicited inbound connections. Gateways, proxies, VPNs, and correctly configured firewalls present nonetheless different architectures for controlling what can attain OT tools. The essential query is due to this fact not merely whether or not an OT system is “linked to the Internet,” however what paths exist by the encompassing community for an unsolicited connection to succeed in it.
For the OT skilled, figuring out whether or not this publicity exists needn’t require an in depth audit of the encompassing IT roads. The controller itself can present helpful proof. On a JNIOR, for instance, the NETSTAT -M command screens community connections and connection makes an attempt in actual time. Unexpected incoming connection makes an attempt from public IP addresses are direct proof that some path by the community exists. If an edge controller sitting behind what’s believed to be a protecting firewall instantly begins reporting unsolicited connection makes an attempt from public IP addresses, there’s something value investigating.
If surprising Internet visitors is reaching an edge controller, it is very important enlist the help of community personnel. There could also be one thing upstream that may be accomplished, and others want to pay attention to the publicity. But the controller needn’t stay a passive participant. There are issues it may possibly do for itself.
>> A Cloak of Invisibility?
There isn’t any scarcity of established cybersecurity recommendation. Change default passwords. Eliminate unused accounts. Disable providers and protocols that aren’t required. Require authentication the place it’s accessible. Restrict entry by firewalls and different community controls. All of those measures are essential, and CISA is correct to bolster them. [2] But that is well-traveled floor. The cybersecurity business has been repeating a lot of this recommendation for years, and there may be little worth in beating that exact horse once more right here.
Consider as an alternative the strategic worth of invisibility. Much of the malicious exercise circulating on the Internet is automated community reconnaissance—in search of targets moderately than attacking a particularly chosen one. Every response offers data. A reply to a PING confirms that one thing is there. A SYN-ACK packet confirms {that a} TCP service is listening. A protocol response could determine the service and maybe even the tools behind it. With every alternate, an nameless scanner learns one thing extra whereas the controller expends sources offering the lesson.
What if the controller might stay absolutely accessible to reliable customers whereas showing invisible to a lot of that reconnaissance? Such a functionality wouldn’t exchange passwords, authentication, encryption, or firewalls. Nor would it not make the controller invisible to a decided adversary who already knew the place to look. But towards the large background inhabitants looking blindly for its subsequent goal, invisibility offers a major strategic benefit. An edge controller has no obligation to announce its presence, determine its providers, or spend sources responding to each stranger who knocks.
This deserves to be a part of the cybersecurity dialog. Before requiring extra processing energy to execute stronger defenses towards each connection try, we should always ask what number of of these connections have to be entertained within the first place. Reducing the assault floor is nice. Reducing the inhabitants that may uncover that assault floor is best nonetheless.
And this isn’t theoretical. JANOS already offers the JNIOR with such a cloak. It requires no extra {hardware}, no gateway, no cloud service, and no more and more complicated cryptographic algorithm. The functionality known as SYN greylisting.
>> SYN Greylisting: Don’t Answer Every Knock
The concept behind greylisting just isn’t new. Email servers have lengthy used greylisting to reap the benefits of an essential distinction between reliable mail techniques and techniques trying to function at huge scale. A reliable mail server encountering a brief refusal is anticipated to attend and take a look at once more. A system trying to contact hundreds of thousands of potential targets has a really completely different financial incentive. Time spent repeatedly pursuing one uncooperative tackle is time not spent discovering 1000’s of others. Greylisting turns persistence right into a easy take a look at of legitimacy. [3]
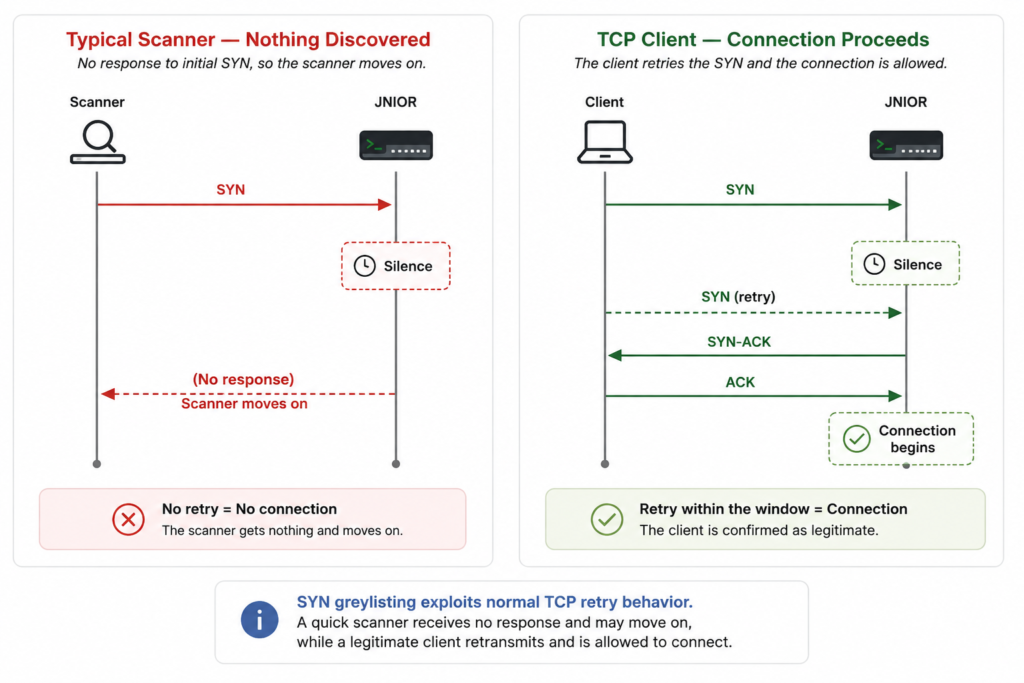
The similar asymmetry exists in automated community reconnaissance and port scanning. A reliable TCP shopper is designed with the belief that packets may be misplaced. If its preliminary SYN receives no response, it retransmits. [4] An automated scanner sweeping hundreds of thousands of IP addresses and ports has little incentive to dedicate the identical period of time to each tackle that continues to be silent. Many due to this fact ship a probe, wait briefly for a response, and transfer on. Forcing a retry imposes a small value on a reliable shopper, however multiplied throughout hundreds of thousands of potential targets, it imposes extra value on the scanner as nicely.
JANOS SYN greylisting exploits precisely that conduct. When enabled, the preliminary SYN packet requesting connection to an open port is intentionally ignored. No SYN-ACK packet is returned. To a scanner performing a fast sweep, there could seem like nothing there. A reliable shopper, nonetheless, retransmits its SYN connection request as TCP was designed to do. If that retry arrives inside an applicable window—not suspiciously quick and never so late that the unique try has been forgotten—JANOS permits the connection to proceed. No whitelist administration is required. The similar shopper should exhibit the identical easy conduct the following time it initiates a connection. The connection delay has minimal affect.
The result’s a remarkably cheap filter requiring little or no code within the TCP driver itself. Because it operates at that stage, the safety mechanically applies throughout listening ports and protocols earlier than authentication, encryption, protocol processing, or software software program turns into concerned. There isn’t any whitelist to take care of and no extra safety service to configure. The controller doesn’t have to find out whether or not the stranger is malicious. It merely asks the stranger to exhibit a small quantity of persistence earlier than agreeing to spend sources on the dialog. For as soon as, a number of the value of initiating an undesirable interplay has been shifted away from the controller and again towards the stranger knocking on its door.
An automated scanner can, in fact, be designed to retry. SYN greylisting just isn’t supposed to be an impenetrable barrier. Its worth is in refusing to make reconnaissance easy. Scanners that don’t retry obtain nothing. Those that adapt should generate extra visitors and dedicate extra sources to the duty. Older automated instruments, malware, and worms that by no means anticipated such conduct could merely fail to find the system in any respect. The goal is to not make reconnaissance unimaginable, however to cease making it unnecessarily straightforward.
That raises a bigger query: why ought to this functionality be restricted to JANOS?
>> What Happens When You Drop the Shields?
There is an apparent method to decide whether or not SYN greylisting is definitely undertaking something: flip it off. We did precisely that on one of many JNIORs deliberately working on a public IP tackle. With the safety enabled, the controller routinely spends about 95 % of its processor time idle even whereas the encompassing Internet stays busy with reconnaissance and malicious visitors.
With SYN greylisting disabled, that modified dramatically. Automated connection makes an attempt started progressing into the providers themselves. SSH was significantly costly. Each incoming connection might provoke a number of seconds of public-key cryptography earlier than authentication was even tried. At instances, SSH consumed roughly 95 % of the accessible processor sources. During the in a single day take a look at, the buildup of SSH exercise finally prevented processes from yielding for lengthy sufficient that the JANOS course of watchdog interpreted the situation as a failure and rebooted the controller. The system log recognized the trigger: “SSH Server brought about watchdog reset.”
The following morning, we went a step additional and disabled the separate IP Blacklister as nicely. The outcome supplied an unobstructed view of the background Internet. SSH password assaults continued connection after connection. Other shoppers tried command-line credentials, internet exploits, TLS negotiations, protocol probes, and various reconnaissance. One SSH supply methodically tried a succession of root passwords, establishing a safe connection for every try and forcing the controller to carry out the related cryptographic work earlier than in the end failing authentication.
The controller continued doing its job, however the impact was apparent to a reliable consumer. Interactive SSH response grew to become intermittent sufficient that at instances the controller appeared to have stopped responding. Eventually the requested command would execute. The processor had merely been busy servicing strangers. For an OT controller, that’s greater than an inconvenience. Processor time being unpredictably diverted into community safety immediately challenges the objective of deterministic operation. The controller’s first accountability stays the method it was put in to watch and management.
Our take a look at JNIOR was intentionally linked utilizing a public IP tackle in order that the exercise may very well be noticed with out an upstream firewall hiding any of it. That is the acute case, however the challenge just isn’t restricted to controllers linked that means. A service uncovered by port forwarding presents the identical listening port to the general public Internet. If unsolicited visitors can attain that port, the controller should take care of it whatever the community structure that delivered it.
This illustrates an essential distinction. Strong authentication can stop an attacker from gaining entry, however it doesn’t essentially stop an attacker from consuming the sources required to succeed in authentication. The strongest password within the globe does nothing to recuperate the processor time spent figuring out that the password was unsuitable.
With SYN greylisting restored, most of these interactions as soon as once more disappear earlier than SSH, TLS, the online server, or software software program ever develop into concerned. The assault has not been defeated by stronger cryptography. For the overwhelming majority of automated connection makes an attempt, it merely by no means will get began.
>> Let’s Turn the Tables
Industrial cybersecurity can’t develop into an countless contest wherein each enhance in malicious exercise is answered by requiring the controller to carry out nonetheless extra work. Stronger cryptography, extra subtle authentication, and more and more complicated safety protocols all have their place. They additionally devour sources. In OT, these sources had been bought first to watch and management a course of, and the expectation is that they’ll proceed doing so deterministically for a few years.
SYN greylisting demonstrates one other mind-set about the issue. It doesn’t try to determine the attacker. It doesn’t examine a rising database of threats. It doesn’t require one other processor, gateway, subscription, or cloud service. It merely exploits the conduct of reliable TCP shoppers to keep away from participating with a big inhabitants of automated reconnaissance within the first place. A protection needn’t be impenetrable to be worthwhile. Sometimes merely refusing to cooperate adjustments the equation.
JANOS has served as a proving floor for this method, however SYN greylisting mustn’t stay a JNIOR curiosity. It deserves consideration as a defensive functionality in embedded TCP/IP stacks usually. Widespread use might frustrate present scanners, malware, and worms that don’t retry whereas forcing newer reconnaissance instruments to expend extra effort. Legitimate TCP shoppers already know tips on how to get by. And the implementation can happen earlier than costly authentication, encryption, or software processing ever begins.
Perhaps the bigger lesson is that we have to broaden the economic cybersecurity dialog. We ought to proceed making authentication stronger and communications safer. But we should always dedicate equal creativity to defenses that devour fewer sources, cut back pointless interplay, protect determinism, and shift a number of the burden again towards these producing the malicious visitors.
CISA has made clear how severe the issue has develop into. SYN greylisting demonstrates that stronger safety doesn’t at all times require stronger {hardware}, extra computation, or one other layer of complexity. Sometimes the higher protection is solely to know how the assault works and refuse to cooperate with it. The method is cheap, the underlying TCP conduct already exists, and we have now demonstrated that it really works.
If a number of traces of code in a TCP stack can stop this a lot malicious exercise from ever getting began, what are we ready for?
>>
References
- Cybersecurity and Infrastructure Security Agency (CISA) et al., Primary Mitigations to Reduce Cyber Threats to Operational Technology, May 6, 2025. U.S. Cybersecurity and Infrastructure Security Agency.
- Cybersecurity and Infrastructure Security Agency (CISA), Internet Exposure Reduction Guidance, June 4, 2025. U.S. Cybersecurity and Infrastructure Security Agency.
- M. Kucherawy and D. Crocker, Email Greylisting: An Applicability Statement for SMTP, RFC 6647, Internet Engineering Task Force, June 2012.
- W. Eddy, ed., Transmission Control Protocol (TCP), RFC 9293, Internet Engineering Task Force, August 2022.