Microsoft Defender has stronger protections you most likely aren’t utilizing
Windows Security does greater than scan for viruses, however surprisingly, a few of its stronger protections aren’t necessarily active in your PC by default. There’s normally a cause, since just a few of them can block your apps and even trigger compatibility issues.
I assumed the essential ones had been already taken care of as a result of Windows Security consistently notifies me to take motion. So I just lately checked all of them on my PC and seen 4 had been off by default, and one wasn’t even listed.
Memory Integrity
Hidden till I modified a BIOS setting
Memory Integrity, additionally referred to as Hypervisor-protected Code Integrity (HVCI), makes use of virtualization-based safety to run kernel-mode integrity checks on drivers and different code earlier than they’ll run inside essential, high-security elements of Windows. This, in flip, retains malicious code out. You’ll discover it below Windows Security -> Device safety -> Core isolation particulars.
On my laptop computer, nevertheless, it wasn’t even listed in any respect. I initially thought my laptop computer’s {hardware} did not help it, however the issue was that virtualization was switched off within the BIOS.
So, I enabled Virtualization Technology in the BIOS, and Memory Integrity confirmed up, set to “Off.” I turned on the toggle, restarted, and it now exhibits as “On.” I additionally checked Device Manager to see if there are any driver points and located no warning icons.
If it’s lacking in your PC too, verify the Performance tab in Task Manager to see if virtualization is enabled earlier than assuming your {hardware} does not help it. You could have to allow Virtualization Technology (VTx) on Intel and SVM Mode on AMD. Just change solely that setting and go away all the things else alone within the BIOS.
Back up your PC earlier than making adjustments within the BIOS. Mistakes can disrupt and even cease your PC from booting.
LSA safety
One extra layer on your login

The Local Security Authority is the a part of Windows that handles sign-ins and retains your login credentials in reminiscence when you’re signed in. This makes it a first-rate goal for credential-stealing attackers.
A stolen credential can let somebody sign up as you. So, LSA protects you by stopping unassigned drivers and plug-ins from loading. It’s proper below Memory Integrity on the identical Core isolation particulars web page.
Mine was off, with a warning below it that my system could also be susceptible. The warning doesn’t suggest my credentials had been uncovered; it simply means the safety wasn’t energetic. You want to avoid wasting your work first as a result of Windows will not apply the settings till you restart.
You have to be careful for compatibility, although. Older safety or different elements that aren’t correctly signed might cease loading as soon as LSA is on. It can be common to run into LSA protection errors after a restart, though I have never run into something like that to date.
Smart App Control
Upgraded PCs was once locked out

Smart App Control takes a stricter strategy to apps than merely scanning for recognized malware. It blocks apps Microsoft can not confirm as secure, together with unsigned ones. You can discover it below App & browser management > Smart App Control settings, with three choices: On, Off, and Evaluation.
In Evaluation mode, Windows learns whether or not it may shield you with out getting in your approach, then turns Smart App Control on or off itself. However, the Evaluation mode was greyed out on my PC.
For years, it was restricted as a result of it labored on clear installs of Windows 11, and when you turned it off, you could not flip it again on with out reinstalling. That meant individuals who had upgraded their PCs could not merely change it on later.
That’s now not the case, as Microsoft introduced a change in 2026, so an upgraded PC like mine is not essentially locked out anymore.
But it comes with a catch, particularly should you check apps quite a bit. If you typically obtain software program from unfamiliar sources, it can probably get in your approach.
Controlled folder entry
Handy in opposition to ransomware, with one catch
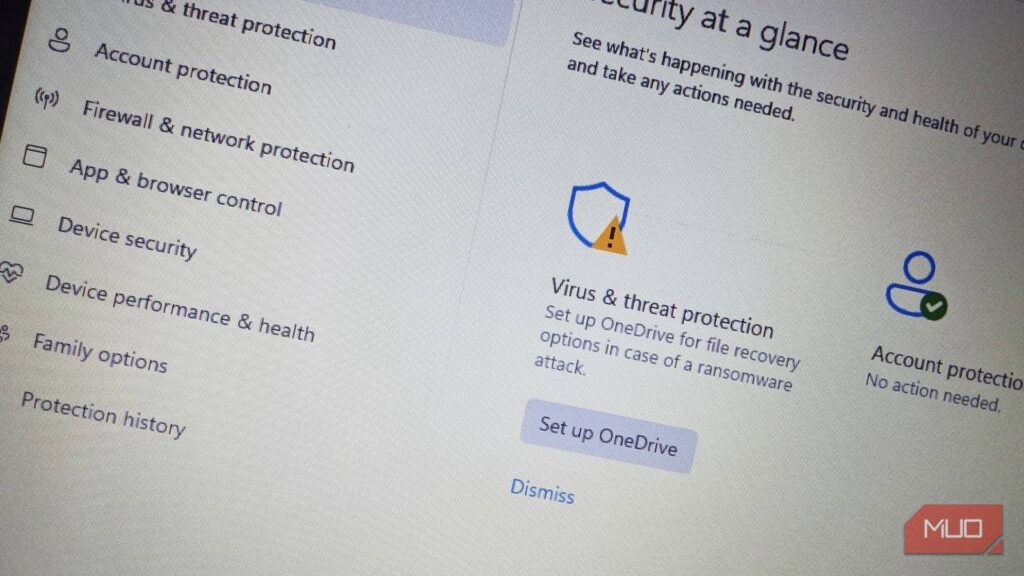
Controlled folder entry stops apps Windows doesn’t belief from altering information in protected folders reminiscent of Documents, Pictures, and Videos, which is what ransomware must lock your information. You’ll discover it in Virus & risk safety -> Manage ransomware safety. You can even add your personal folders to the protected listing there.
Most apps get via with out points, since Windows permits those it considers secure. Once I turned it on, it logged a protected-folder-access block whereas I used to be utilizing Android DeX. It was marked as low severity. I additionally obtained a suggestion to arrange OneDrive for file restoration.
The catch is that Controlled folder entry can cease you from saving information from apps you belief, which is why it is off by default. If that occurs, you possibly can simply add the app below Allow an app via Controlled folder entry. That’s one thing to remember should you repeatedly use older or much less widespread apps. That’s a good commerce for me to protect against ransomware.
Potentially undesirable app blocking
Microsoft says it is on by default

Potentially undesirable apps (PUAs) aren’t essentially malware, however they’ll set up undesirable apps, show sudden advertisements, or trigger different issues. Those low-reputation toolbars and bloatware that experience together with free installers. You’ll discover this setting in Apps & browser management -> Reputation-based safety settings.
Microsoft’s support page says PUA has been on by default since August 2021. So it was stunning that it was off on my PC, with the identical warning that my system could also be susceptible, and I do not know why. After enabling it, you must verify the packing containers beneath to dam apps and downloads.
The solely problem right here is {that a} professional instrument with little status can get flagged too. This is essential should you obtain from much less acquainted sources. Windows really retains a listing of what it blocks in Protection historical past, so you possibly can assessment it.
Worth a glance by yourself PC
I counsel enabling these one by one; if one thing breaks, you may know which setting brought on it.
Everything has continued working after I enabled them on mine, and the Device Manager hasn’t flagged something. Only the Controlled folder entry blocking has been my intervention to date.
If you have had a Windows 11 laptop computer for years, particularly if it was upgraded reasonably than freshly put in, open Windows Security and verify these settings your self. You could discover that a few of the protections you assumed had been energetic aren’t.