Each manner advertising and marketing emails observe you and the way to cease them
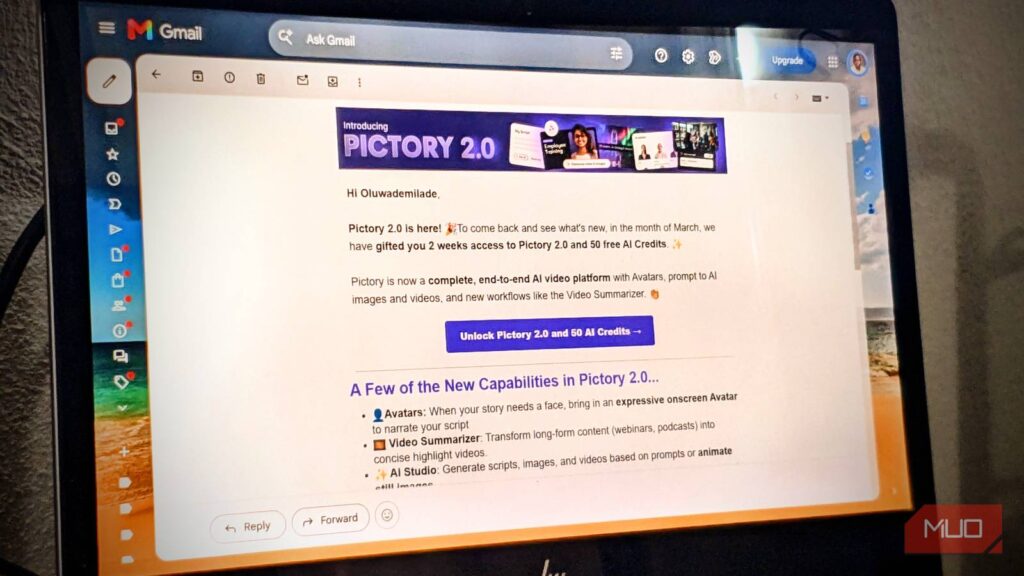
Say a retailer emails you 20% off one thing you checked out as soon as. You open it, skim it for 5 seconds, and shut it with out tapping something. Even although you barely interacted with it, that fast peek seemingly confirmed up on the corporate’s advertising and marketing dashboard.
Marketing emails can observe opens, hyperlink clicks, and different habits, generally earlier than you’ve touched something contained in the message. Most of that plumbing stays fully out of sight, which is why it’s simple to imagine an unopened hyperlink means you left no path. The excellent news is that fashionable e-mail apps have already made among the oldest monitoring methods rather a lot much less dependable, and there are a number of others you may shut down your self.
An open can ship a little bit receipt
The invisible picture doing attendance

Most e-mail monitoring depends on exterior photographs. Instead of saving an image contained in the message, an e-mail hyperlinks to a photograph hosted on an organization’s server. The second your mail app masses that picture, the corporate is aware of you checked out it.
Marketers typically use a tiny, invisible graphic for this, referred to as a 1×1 monitoring pixel. It tells the corporate precisely while you opened the e-mail. This connection may leak your IP tackle and fundamental particulars in regards to the gadget you might be utilizing. However, trackers do not must be invisible; an everyday product picture can observe you a similar manner if the hyperlink has a singular code hooked up.
Because of this, an e-mail “open” does not really imply somebody learn it. It simply means the picture was loaded. Today’s e-mail apps deal with this in another way to guard your privateness:
- Gmail masses photographs via Google’s personal servers as an alternative of connecting on to the sender. This hides your IP tackle, although the sender nonetheless is aware of the picture was fetched.
- Apple makes use of Mail Privacy Protection to obtain e-mail photographs quietly within the background earlier than you even open the message. This makes it seem like you opened the e-mail even for those who by no means touched it.
- Outlook additionally blocks exterior photographs by default or routes them via its personal safe servers.
All of that makes open charges rather a lot murkier than the neat share in a advertising and marketing dashboard suggests. An “open” could be an individual, a proxy, a privateness characteristic, or an automatic fetch, which is a fairly large vary for one little metric.
Clicking leaves a a lot cleaner path
That blue hyperlink has paperwork hooked up

When you click on a hyperlink in an e-mail, it tells entrepreneurs much more than a easy “open” does. That’s as a result of newsletters use distinctive, personalized hyperlinks for each single individual on their mailing listing.
Instead of taking you straight to a retailer’s web site, the hyperlink secretly detours to a advertising and marketing firm’s server first. That server logs your click on, figures out precisely who you might be and which e-mail you got here from, after which zips your browser to the precise webpage. Because of this background magic, you and your good friend may click on the very same button in the identical e-newsletter, however you’d each be clicking completely totally different URLs.
Even so, click on numbers aren’t excellent. Security applications and antivirus software program typically click on hyperlinks robotically to scan them for malware earlier than letting them via. This creates “faux clicks” that look identical to actual human exercise, which advertising and marketing platforms must filter out.
Once the precise webpage masses, common web site monitoring takes over. Cookies, browser scripts, and advert networks begin tracing your steps, however that knowledge belongs to the web site itself, not your e-mail app.
You’ve most likely observed how lengthy and messy these hyperlinks look. Pieces of textual content within the URL like utm_source=e-mail or utm_campaign=summer-sale merely inform the web site’s analytics software program which advertising and marketing marketing campaign introduced you there. On their very own, these “UTM tags” do not know your title or id—however different monitoring codes hidden deeper within the hyperlink can.
Personalized unsubscribe hyperlinks work the identical manner. The e-mail platform wants a singular code to know precisely which individual desires off the listing. If you belief the e-newsletter, clicking that official unsubscribe button is one of the simplest ways to cease getting their mail.
However, spam and phishing emails are a very totally different story. If an e-mail seems shady or untrustworthy, don’t click on something inside it. Even clicking “unsubscribe” on a rip-off e-mail lets the sender know your inbox is lively, giving them the precise response they need.
Make your inbox a worse informant
A couple of settings do a lot of the work
You don’t have to surrender HTML e-mail or dissect each URL prefer it’s proof in against the law lab. A couple of habits lower out a whole lot of the simple monitoring with out making your inbox depressing to make use of.
- Stop exterior photographs from loading robotically. Gmail has an Ask earlier than displaying exterior photographs possibility, and changing this Gmail setting can stop hidden tracking images from loading automatically.
- Keep your mail app’s privateness options turned on: If you utilize Apple Mail, navigate to Apps > Mail, then faucet Privacy Protection and toggle on Protect Mail Activity. If you utilize Outlook, make certain your exterior picture controls are activated. Go to Settings > Privacy and knowledge > External photographs, and tick the circle subsequent to Always use the Outlook service to load photographs.
- Use tracker blocking when your mail app helps it: If your present e-mail app doesn’t already block monitoring pixels, there are several easy ways to do so.
- Go straight to the web site while you don’t need to use the e-mail hyperlink: If a model sends you a coupon or e-newsletter, don’t click on the hyperlink within the e-mail. Instead, open your browser, seek for the shop, or kind their internet tackle straight into the search bar.
- Check sketchy hyperlinks earlier than opening them: Look at a hyperlink earlier than you click on it. If you might be on an Android telephone, apps like URLCheck can let you safely inspect messy, tracking-heavy links earlier than they open.
- Try a privacy-first e-mail service: If you might be really fed up with monitoring, think about switching to a supplier like Proton Mail, which has built-in tools specifically designed to block email trackers.
- Use aliases for newsletters and on-line accounts that do not want your major tackle: Keeping your real email address off random websites additionally makes it simpler to retire an alias that begins attracting junk.
Suspicious e-mail is simpler to take care of. Mark it as spam or phishing and don’t click on something inside it, together with the unsubscribe button. Some innocent-looking email habits can create openings for attackers, and an unknown sender doesn’t want a courtesy click on simply because the message seems polished.
You additionally don’t have to make use of each precaution on each e-newsletter. You can save the stricter settings for senders you don’t know or don’t belief, whereas letting the mail you really need behave usually.
Your inbox does not must report for obligation
Marketing emails have at all times been a two-way road. An organization provides you a reduction code, a product replace, or another cause to pop into your inbox, and in return, they hope you’ll finally purchase one thing from them.
Once you notice simply how a lot monitoring and knowledge assortment occurs behind the scenes of that deal, it will get rather a lot simpler to determine how a lot privateness you’re keen to surrender. You do not must deal with each e-newsletter like malicious spyware and adware. Just keep in mind that behind each cheerful “20% off” button, there’s an entire digital accounting division taking notes.