Every main browser has a setting that may fully punch via your network-wide DNS filtering
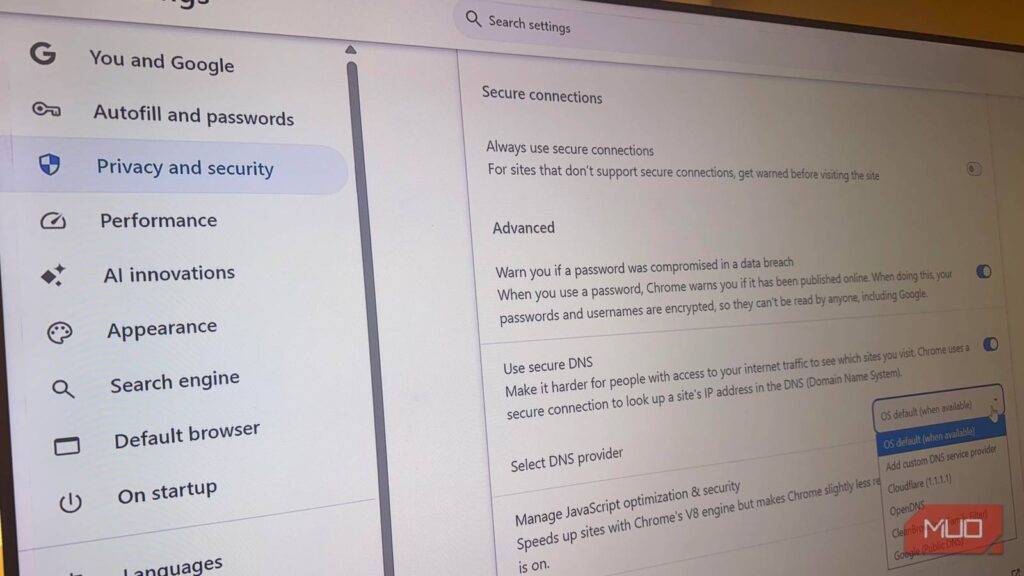

I put one among my favourite soccer web sites on my NextDNS deny record and, as anticipated, Windows might now not resolve the area usually. But when I opened Chrome and flipped just one setting, the browser loaded the location as if the block had by no means existed.
Out of curiosity, I attempted this experiment in Edge and Firefox and acquired an identical outcomes. You could have arrange DNS filtering to maintain adverts, trackers, or sure websites off your community, however it would not assure your browser will respect it. One 15-second examine could reveal this conduct.
The silent log
One toggle, one PC, two fully completely different outcomes
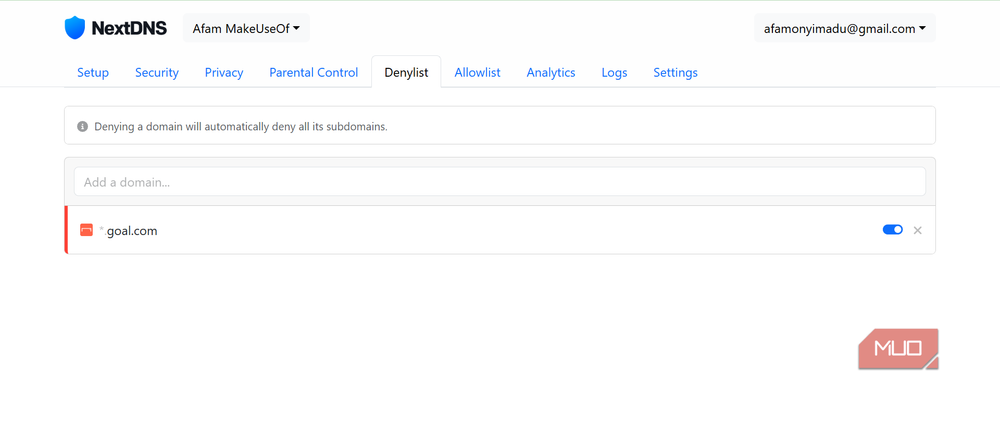
I wanted to run my check on a clear baseline. So I added aim.com to the deny record of NextDNS, my DNS filtering and security service, and immediately I might now not resolve aim.com usually. The DNS lookup for aim.com was returning 0.0.0.0. I confirmed this by checking the NextDNS logs, which confirmed the requests have been blocked, as anticipated.
Then I opened Chrome and navigated to chrome://settings/safety, chosen an exterior DNS supplier, Google (Public DNS), and reloaded the aim.com web page. It loaded as if NextDNS hadn’t blocked it.
When I checked the NextDNS logs, there was no blocked entry, and in reality, no entry in any respect. The filter acted prefer it did not know that request ever existed.
So I attempted the identical sequence on Edge and Firefox, and the outcomes have been an identical:
|
Browser |
Secure DNS utilizing an exterior supplier |
Secure DNS off |
|---|---|---|
|
Chrome |
Loads, no log entry |
Blocked, entry seems |
|
Edge |
Loads, no log entry |
Blocked, entry seems |
|
Firefox |
Loads, no log entry |
Blocked, entry seems |
Switching off Use safe DNS or setting Select DNS supplier to OS default (when accessible) introduced again the block immediately.
The check confirmed that the browser can resolve a site with out consulting my DNS filter when Secure DNS is configured to make use of an exterior resolver. I’m not saying different community controls cannot block entry; firewall guidelines or IP-based blocks would possibly nonetheless apply. This is a slender however efficient bypass.
The facet door
How the browser stopped utilizing your community’s DNS
The request path when Secure DNS is disabled appears like this: Browser → Windows DNS → NextDNS → blocked.
When it is enabled, it appears like this: Browser → exterior DoH resolver → DNS response.
When a browser makes use of the system’s DNS resolver, the area lookup finally reaches the resolver configured on your system. That’s the place a DNS filter like mine can apply its guidelines. Once Secure DNS is about to an outdoor supplier, that handoff now not occurs in most browsers, together with Chrome, Firefox, and Edge, which I examined.
In these circumstances, the browser sends the DNS lookup via an encrypted DoH (DNS-over-HTTPS) connection to the resolver configured in its Secure DNS settings. So, whereas the connection was nonetheless there, the browser merely stopped asking my filter.
By design, it is not sneaky. One aim of encrypted DNS is to stop your ISP or somebody operating a public Wi-Fi community from seeing your DNS lookups in plaintext. It’s a good aim, however it additionally sidesteps filters that depend on seeing these DNS lookups.
In my case, the filter ran on my PC. But since Mozilla paperwork that DNS-over-HTTPS can bypass network or native DNS filtering, it most likely will apply to different setups.
Firefox has safeguards that may disable DoH in some community configurations.
Every browser, completely different door
Chrome, Edge, and Firefox every take their very own route
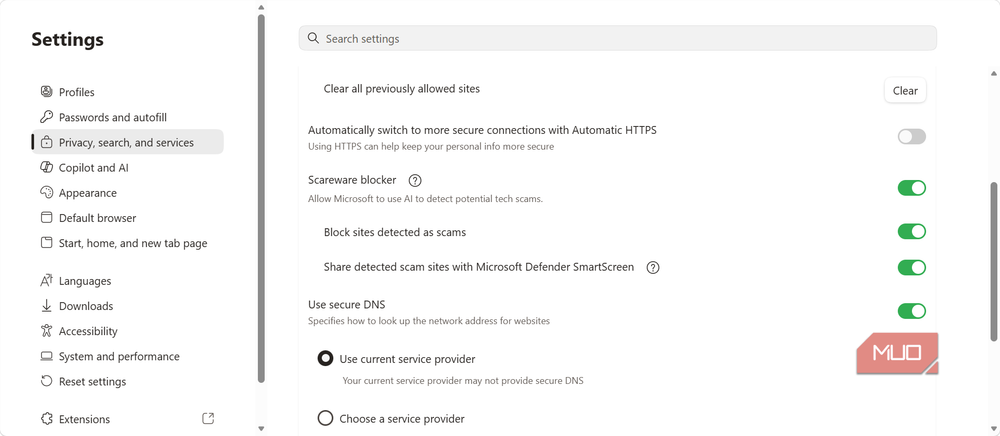
On Chrome and Edge, it is referred to as Secure DNS. Brave runs on the identical engine and in addition calls it Secure DNS.
In Chrome and Edge, you get the total bypass by selecting a supplier your self, similar to I did. In computerized mode, each Chrome and Edge can fall again to the system’s common DNS if the safe lookup fails. Choosing a particular Secure DNS supplier removes that fallback.
It works barely in a different way on Firefox. Default safety mode could disable DoH if it detects parental controls or community alerts requiring it to not use safe DNS. I choose Custom safety to decide on the resolver and hold safe DNS lively. I can take it a step additional by deciding on Max safety, which makes Firefox strictly refuse to fall again to the system DNS even when a safe connection is unreachable.
The necessary two-minute examine
Even if you do not have my precise setup, you possibly can nonetheless examine who truly answered your browser. Open your filter’s question log and cargo any website you have not visited in that browser. Use a site you have not just lately visited in that browser, as a result of in case you get a response from the cache, a working setup could look damaged.
You know the DNS filter utilized the rule and is doing its job if the question exhibits up as blocked. If it exhibits up as allowed, the DNS filter noticed the lookup however did not block it. When it by no means seems within the filter’s logs whereas the web page masses, that is sturdy proof that this browser did not use that DNS filter for the lookup.
The route would change in case you toggle Secure DNS and cargo a brand new area. But your subsequent steps needs to be guided by what you truly need. You could flip the setting off or level the browser’s Secure DNS setting to your filter’s encrypted DNS endpoint (if it supplies one) if you would like filtering. On the opposite hand, you allow the DNS selections exterior your filter to prioritize privateness.
However, the purpose is that you do not have to rebuild your community simply because one browser ignores your filter. It’s extra necessary to first discover out who’s answering its DNS queries.