Changing your DNS makes looking safer, however it received’t cover your historical past from the individuals who matter most
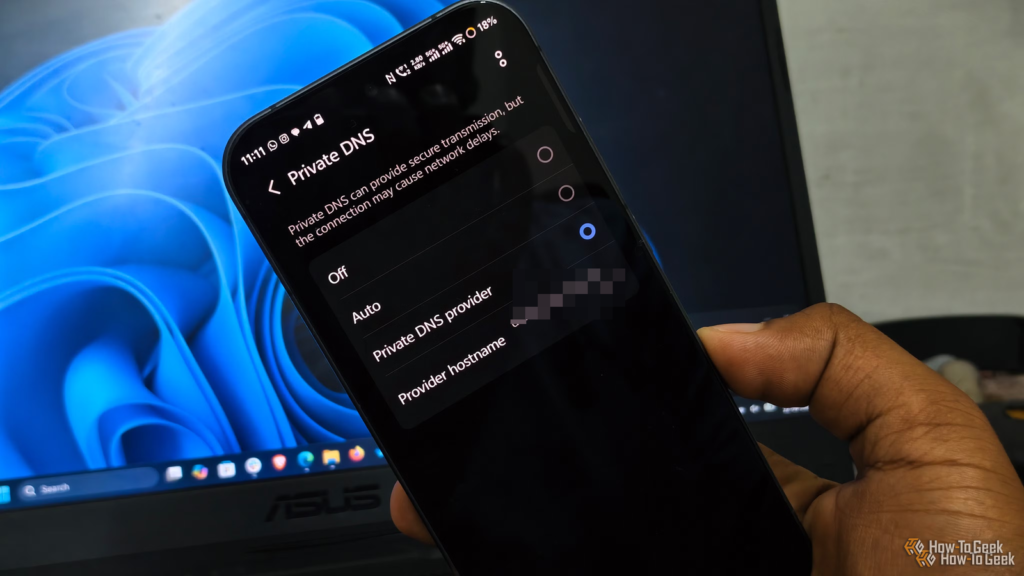
Changing your DNS server is a kind of easy networking tweaks that may make looking safer, however DNS privateness is straightforward to misconceive. Changing your DNS supplier doesn’t make your looking historical past invisible. Your ISP, employer, college, or community administrator should produce other methods to find out which providers you might be connecting to.
DNS solely tells your laptop the place to attach
Changing DNS modifications the resolver, not the connection itself
The primary job of DNS is to translate a site comparable to instance.com into an IP tackle that your laptop can hook up with. When you employ your ISP’s DNS server, the ISP handles these lookups. When you configure your machine to make use of Cloudflare or Google, these firms deal with them as a substitute.
That will be helpful for privateness. If you employ DNS over HTTPS (DoH) or DNS over TLS (DoT), the question between your machine and the resolver is encrypted. Someone monitoring the native community can now not merely learn the DNS packets and see each area being requested, however DNS doesn’t carry the remainder of your net site visitors.
After resolving instance.com, your laptop nonetheless wants to hook up with the ensuing IP tackle. Those packets nonetheless must journey by your ISP if you’re utilizing an bizarre web connection. Changing the DNS resolver doesn’t encrypt these packets, cover their vacation spot IP addresses, or flip your connection right into a VPN.
Your ISP can nonetheless see loads
HTTPS protects content material, not essentially your vacation spot
Even when your DNS queries are encrypted, your ISP nonetheless sits between your community and the remainder of the web. For a traditional HTTPS connection, your ISP can not merely learn the contents of the pages you go to. HTTPS encrypts the precise utility information between your browser and the web site.
However, your ISP can nonetheless see the IP addresses your connection communicates with. That can generally reveal the service you might be utilizing. An IP tackle shared by 1000’s of internet sites could not inform the ISP precisely which web site you visited, whereas an tackle devoted to a selected service can present a a lot stronger clue.
TLS has traditionally offered one other supply of knowledge. With conventional TLS connections, the browser can embody the hostname it needs to hook up with within the ClientHello message by Server Name Indication, or SNI. The contents of the HTTPS session stay encrypted, however the hostname in SNI has traditionally been seen to somebody observing the connection.
This is the place Encrypted Client Hello, or ECH, is available in. ECH is designed to encrypt delicate components of the TLS ClientHello, together with info that may in any other case expose the requested hostname by SNI. ECH is a crucial growth, however it isn’t a common privateness change. Its effectiveness is dependent upon help from the browser, server, and surrounding utilities.
Traffic evaluation can present one other supply of knowledge. Even when the contents of a connection are encrypted, the dimensions, timing, and route of packets can reveal traits concerning the connection. An ISP doesn’t essentially have to learn your HTTP requests to know that your machine is speaking with a selected service. So encrypted DNS solves an actual drawback, however it doesn’t make your ISP blind to your web exercise.
Changing DNS means trusting another person
The new resolver can nonetheless see your queries

Another easy-to-miss consequence of switching DNS suppliers is that queries do not disappear. If you cease utilizing your ISP’s resolver and begin utilizing Cloudflare, Cloudflare turns into the resolver receiving these requests. If you employ Google Public DNS, Google receives them as a substitute.
DoH and DoT defend the queries whereas they journey between your machine and the resolver. The resolver nonetheless must see the request to reply it. That makes the supplier’s privateness coverage, logging practices, and jurisdiction related. A DNS supplier operates beneath the legal guidelines relevant to its trade and utilities, which might have an effect on the way it responds to authorized requests for info. This doesn’t imply each public DNS supplier retains an intensive report of all the pieces you do. Their insurance policies differ, and a few DNS suppliers are extra privacy-oriented.
So who can see what?
Privacy is dependent upon who you are attempting to cover from

If you might be utilizing Wi-Fi at a espresso store and have encrypted DNS and HTTPS enabled, the particular person working the community can not merely open a log and skim the pages you visited. They can nonetheless see that your machine is speaking with explicit IP addresses, however they can’t usually learn the contents of your HTTPS session, such because the pages you considered.
Your ISP has significantly extra visibility as a result of it carries your web site visitors. Depending on the connection, the ISP may additionally see SNI and might analyze connection timing and site visitors patterns. In sensible phrases, altering DNS doesn’t cease your ISP from constructing a helpful image of your web exercise.
An organization or college controlling the community can have much more visibility. It can block outdoors DNS, log connections, or use managed-device software program and TLS inspection to examine site visitors. In that setting, altering the DNS setting in your laptop computer could accomplish nothing as a result of the community can override or ignore it.
A VPN modifications the scenario as a result of your ISP sees an encrypted connection to the VPN reasonably than the person locations inside it, however now the VPN supplier is the celebration it’s a must to belief. It can probably see the locations your site visitors reaches, and your DNS configuration can still leak information outdoors the tunnel if the VPN is misconfigured.
DNS privateness has limits
There remains to be a sensible safety profit to selecting a distinct resolver. Some providers can block known malicious domains, which might forestall your machine from connecting to sure malware or phishing websites. Just consider it as selecting a distinct service to deal with DNS reasonably than as a strategy to disappear out of your ISP’s view. If your purpose is to cover the place you go surfing from the community carrying your site visitors, you want to defend greater than DNS.