France’s Grocery store Fridges Were Susceptible Online for Months
On the evening of October 11 to 12, 2026, fridges and freezers in a whole lot of French supermarkets began to heat up. Cyber attackers had pushed the refrigeration techniques into defrost mode, which heats the cooling components to soften ice. Some items reached 50°C (122°F), some gear began to catch hearth, according to the Paris prosecutor, and shops threw away their fresh and frozen food. The stories pointed to at least one maker of refrigeration controllers, Danfoss (a Danish industrial firm).
We went by way of IPinfo’s weekly Internet scans to look at these techniques earlier than the assault. In this weblog publish we’ll discover among the findings. Here’s the TL;DR:
- France had extra uncovered fridge dashboards than the remainder of the international stage mixed: 1,331, towards 1,197 within the different 72 international locations and territories put collectively.
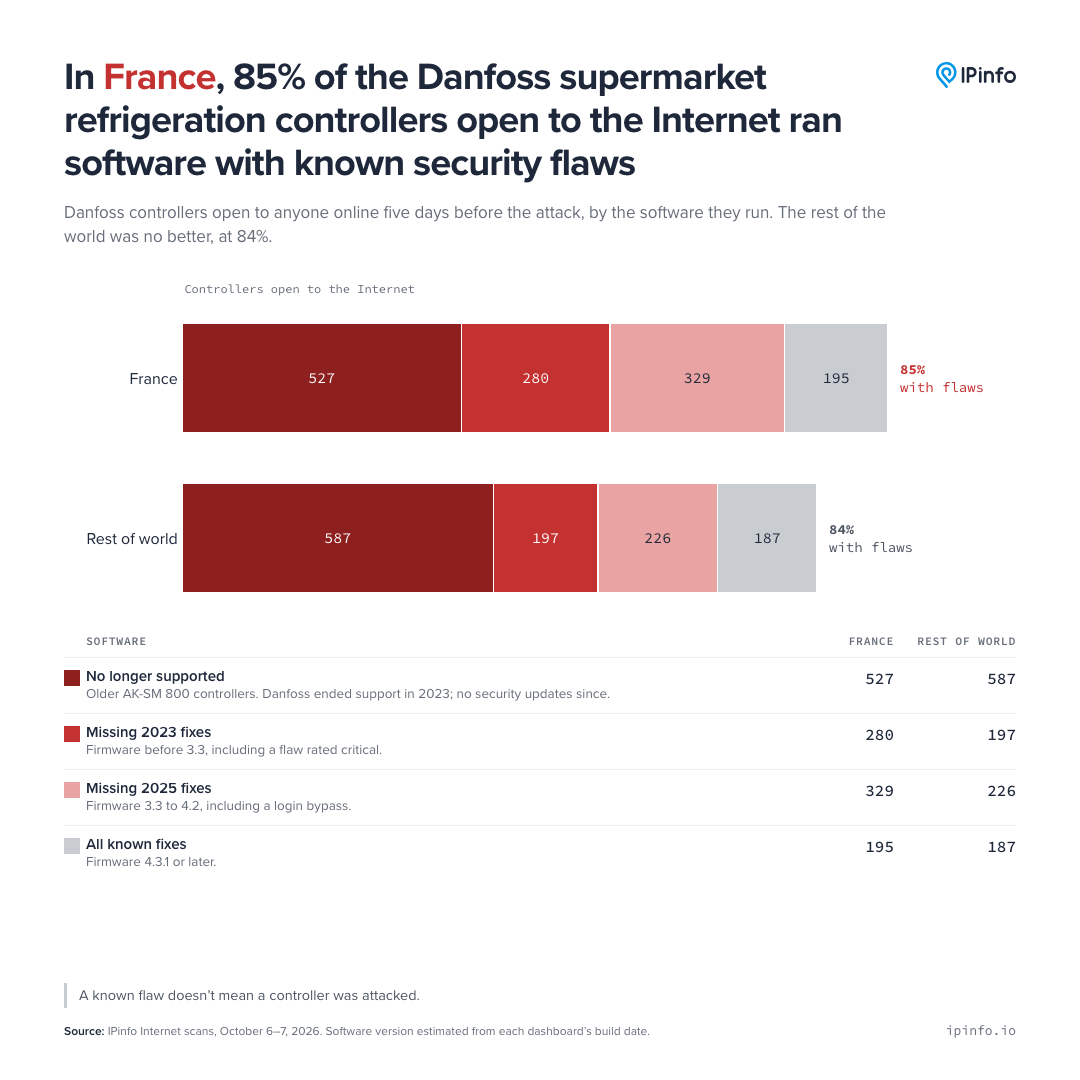
- 85% ran software program with recognized safety flaws. That consists of 527 older controllers Danfoss not helps. Only 195 had each recognized repair.
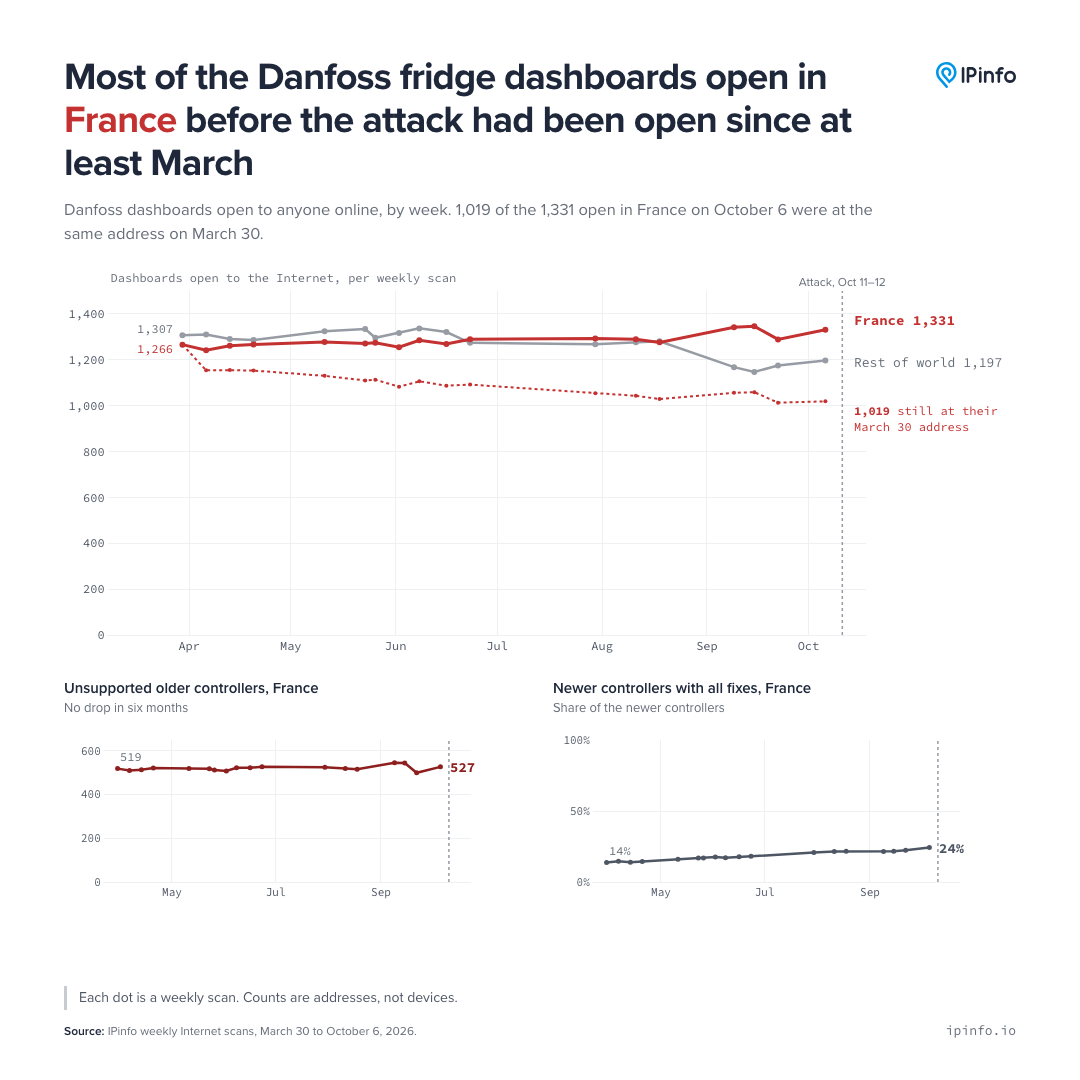
- Most had been uncovered for no less than six months. 1,019 of the French dashboards have been on the similar tackle on March 30, and the share absolutely up to date rose solely from 14% to 24% in that point interval.
- France did not patch worse than different international locations. The flawed share elsewhere was nearly the identical (84%). France simply had much more of those techniques on-line.
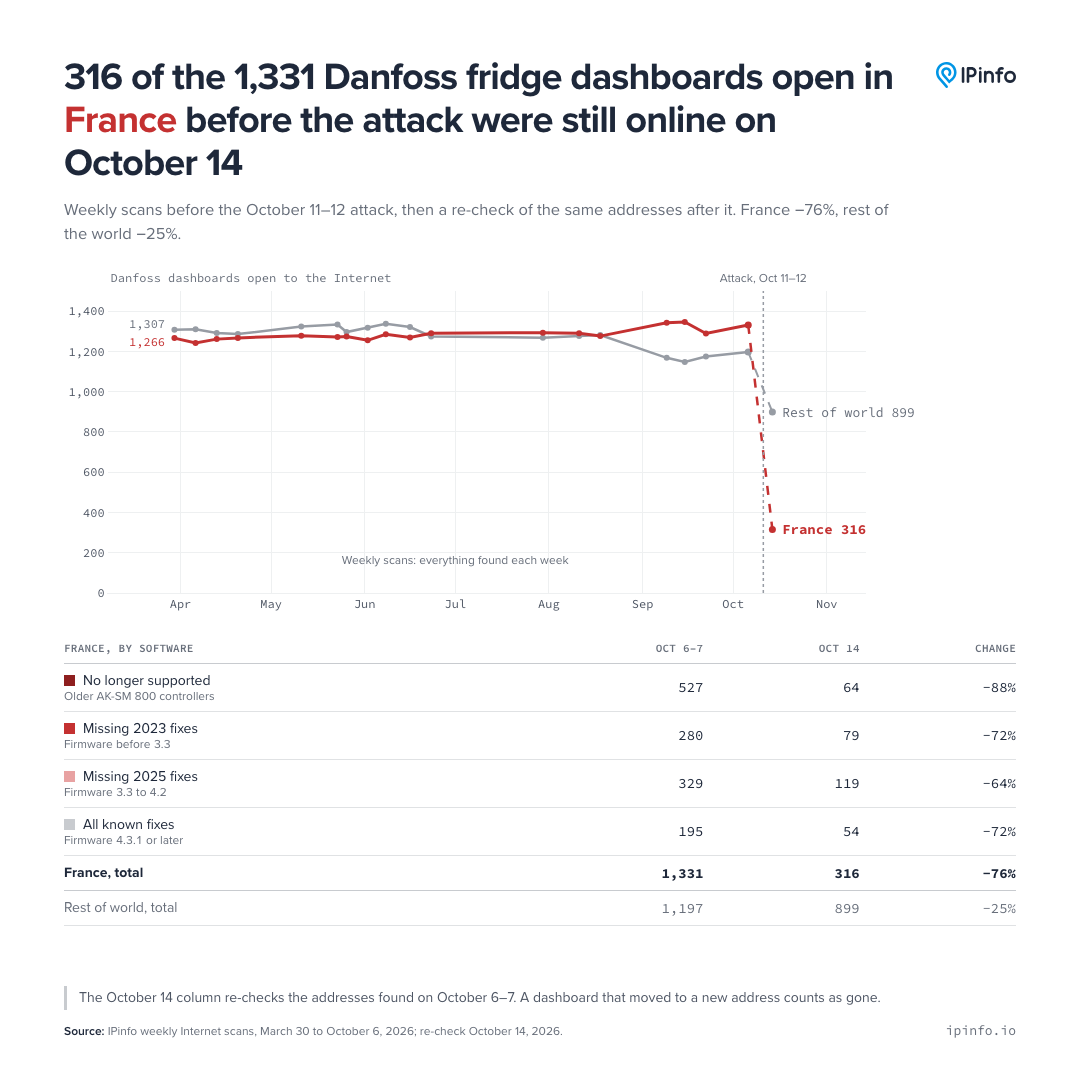
- Most went offline after the assault. 316 of the 1,331 have been nonetheless on-line on October 14.
What Happened
The numbers from the chains continue to grow. More than 400 stores have been hit in whole in keeping with Futura-Sciences, and losses could reach several million euros. Carrefour stated 80 of its shops have been hit, whereas Intermarché and Netto, each a part of Les Mousquetaires (a French retail group), had more than 300 hit. Monoprix reported that about 5% of its stores have been affected.
Leclerc and Coopérative U, two different French grocery store chains, also confirmed attacks. Coopérative U’s CEO, Dominique Schelcher, told RTL that 80 of its 2,000 shops have been hit. He added that the shops do not buy from Danfoss immediately however use a Danfoss system provided by their refrigeration contractors.
Danfoss said a lot of the affected gear was “legacy,” naming two older controller fashions, the AK-SM 800 and AK-SC 355. CERT-FR (France’s cybersecurity company) said it knew of numerous compromises of AK-SM and AK-SC controllers. It informed operators to disconnect them or limit who can attain them, and updated its alert on October 13 so as to add XWEB supervisors (techniques that monitor a retailer’s fridges and freezers) from Copeland, a US maker of cooling gear, and Dixell, its Italian model. Its alert says assault campaigns are in all probability nonetheless ongoing. Nobody has stated who did it or how they obtained in, and the Paris prosecutor’s workplace has opened an investigation.
France Stood Out, by Far
We scan the IPv4 Internet (the commonest kind of Internet tackle) each week, connecting to the standard ports that web sites use (the numbered doorways a pc solutions on) and recording what solutions. In the sweep that ran on October 6 and seven, 5 days earlier than the assault, 2,528 addresses confirmed a Danfoss StoreView dashboard. That is the online web page that shops and technicians use to observe and handle these controllers, the equal of the management panel within the again room, besides that anybody who typed within the tackle may open it.
According to our information, France had 1,331 of them (53%). That is greater than the opposite 72 international locations and territories mixed (1,197). Poland got here subsequent with 179, then the United States (101), Portugal (92), and Belgium (85).
Why France? Our information cannot say, nevertheless it guidelines a couple of issues out. French dashboards ran the identical mixture of software program variations as in every single place else, so that they weren’t patched worse. They additionally weren’t uncommon in how they join. In France, about two-thirds join by way of one nationwide supplier, very like the principle telecom in Portugal, Germany, or Romania. Almost all (98%) are on telecom suppliers’ networks somewhat than in information facilities or clouds, which inserts a controller plugged into the shop’s personal Internet connection, with entry opened for a technician or head workplace.
CERT-FR’s advice hints at why shops preserve them on-line: it tells them to verify their insurance coverage phrases earlier than slicing the information their controllers ship to refrigeration contractors.
Most Fridge Software Was Out of Date
The dashboards additionally give away how previous the software program behind them is. They are available two generations. The older one is a web page constructed with Flash (an previous browser plug-in, retired in 2020) and served by the AK-SM 800. Danfoss declared these controllers end of life in 2023. That similar yr, the safety agency Synacktiv published a login bypass (a means in with out the password) for them, and Danfoss’s recommendation was to limit community entry. This is the “legacy” gear Danfoss named.
The newer one runs on the AK-SM 800A, Danfoss’s present mannequin. Its dashboard reveals when its software program was constructed, a bit just like the manufacturing date stamped on a carton, which tells us roughly which model it runs: 242 of them say May 19, 2023, the construct date of firmware 3.3 (firmware is the software program constructed into the controller). Controllers older than 3.3 miss three 2023 fixes, together with one for a flaw rated critical. Those older than 4.2 additionally miss a repair for a 2025 login bypass, and people older than 4.3.1 miss two more 2025 fixes.
Put collectively, 85% of the French dashboards (1,136 of 1,331) ran software program with recognized safety flaws, nearly the identical because the 84% elsewhere. That is 527 older controllers Danfoss not helps, 280 lacking the 2023 fixes, and 329 lacking the 2025 fixes. Only 195 had each recognized repair.
The Exposure Has Existed for Months
Every scan from late March 2026 till the assault discovered about the identical quantity: between 2,464 and a couple of,622 Danfoss dashboards open to the Internet, roughly half of them in France.
They have been principally the identical units. Of the 1,331 French dashboards discovered on October 6, 1,019 have been open at the exact same tackle on March 30, six months earlier. Over these months, the variety of older controllers Danfoss not helps did not go down in France (519 on the finish of March, 527 in October). Updates got here slowly. The share of newer French controllers with each recognized repair went from 14% to 24%, underneath two factors a month.
Did Stores Disconnect After the Attack?
Most shops did disconnect after the assault. Our subsequent weekly scan ran on October 14, two days after the assault. Of the 1,331 French dashboards from October 6–7, solely 316 have been nonetheless on-line on the similar tackle, a 76% drop. In the weekly scans from August to early October, solely 3% to 7% disappeared from one week to the subsequent. The older controllers Danfoss not helps fell essentially the most, from 527 to 64. Fully up to date ones fell too, from 195 to 54, which factors to shops disconnecting them somewhat than updating them.
Outside France, 25% disappeared, greater than the standard 9% to 12%. Censys, one other Internet scanning firm that counts on daily basis, noticed an identical 71% drop in France between October 11 and 14. On October 14, the technical director of Claroty, the safety firm that discovered the 2025 flaws, told Tom’s Guide that uncovered AK-SM 800 controllers have been nonetheless on-line. Our October 14 scan nonetheless discovered 64 of them.
Where Else These Controllers Are Open
France wasn’t the one nation with these techniques on-line. Danfoss dashboards with recognized flaws have been open in 69 different international locations and territories, led by Poland (157), the United States (85), and Portugal (77). In some international locations most have been the older controllers Danfoss not helps: 80% in Iceland, 75% in Australia, and 72% in Germany.
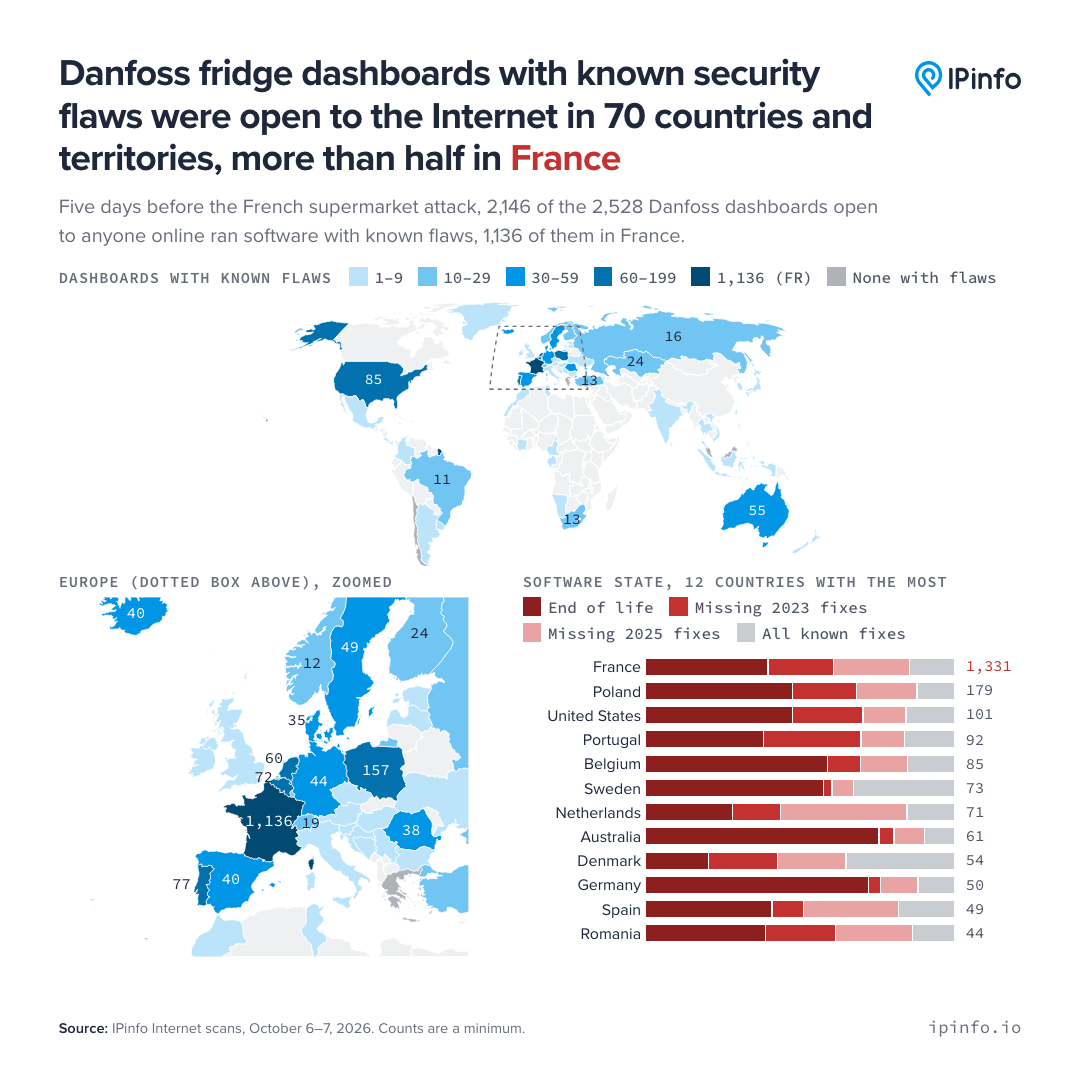
Some stories recommend different European international locations might have been hit. One analyst quoted by Australia’s ABC stated Spain, Portugal, Poland, Germany, and Belgium had additionally been affected. Our information cannot say whether or not they have been, nevertheless it does present that every one 5 had out-of-date Danfoss dashboards open to the Internet 5 days earlier than the assault.
What About Dixell?
CERT-FR’s up to date alert additionally names XWEB supervisors from Dixell, Copeland’s Italian model of refrigeration controllers, so we counted these too. The similar scan discovered 1,611 XWEB dashboards in 66 international locations, however solely 70 in France; Italy, the place Dixell is predicated, had 467. Judging by when their software program was constructed, solely 180 of the 752 newer XWEB PRO items had the February 2026 fixes. The different 859 have been older fashions that haven’t had a software update from Copeland since 2018. After the assault, French operators unplugged their XWEB dashboards too: our October 14 scan discovered solely 20 of the 70 nonetheless on-line, a 71% drop, when a standard week loses 2% to 9%. Elsewhere, together with Italy, the quantity fell solely on the typical weekly price.
How We Counted
The dashboards have been recognized with two fingerprints (patterns that establish a tool) constructed by our information workforce. The newer interface is matched by its web page title. The older one is matched by its internet server plus the Flash loader web page, which identifies the AK-SM 800. AK-SC 355 controllers, which Danfoss additionally named, will not be in our depend. Sixteen units that share the older internet server however aren’t Danfoss (community playing cards in backup energy items, constructing controllers, thermostats) have been eliminated, together with two addresses that reply on nearly each port, an indication of a honeypot (a decoy set as much as appeal to attackers).
An impartial depend by the safety researcher Baptiste Robert, posted on X, discovered 2,752 Danfoss techniques on-line, 1,590 of them in France, just a little above ours. Censys, which scans otherwise, discovered extra: 1,825 of the newer dashboards in France on October 11, 61% of its worldwide whole.
The numbers are a minimal. They cowl IPv4 solely and the ports we scan, and an tackle will not be all the time one retailer. We aren’t publishing any of the addresses. CERT-FR informed us it had already recognized the affected techniques, and we’re in touch with CERT-EU (the EU’s cybersecurity workforce for its establishments) to assist different European cybersecurity groups in any means we are able to.
What Operators Can Do
CERT-FR’s advice is to take these controllers off the general public Internet and, if a contractor wants distant entry, to offer it by way of a safe VPN (a non-public, encrypted connection). Letting in solely the contractor’s addresses is a stopgap, not a repair. A manufacturing facility reset alone is not sufficient both: an uncovered controller that not will get updates will seemingly be compromised once more. For Danfoss techniques, CERT-FR additionally says to replace the firmware, set the safety degree to Strict, and alter the default passwords.
What the Data Can’t Say
We cannot inform from the scans how the attackers obtained in or who they have been, and we do not know which chains or shops have been hit. Being capable of open a dashboard from the Internet doesn’t suggest anybody can break in by way of it, and no person has stated whether or not any of the issues above have been used.
The information does present what issues regarded like earlier than and after the assault. Five days earlier than the assault, France had extra of those dashboards open to anybody than the remainder of the international stage mixed, and most have been behind on updates. After the assault, most of them went offline inside days, and we’ll preserve checking the 316 that have been nonetheless on-line on October 14.
This is one in all IPinfo’s information tales, the place we use our personal measurements to have a look at what occurs on the Internet. If you notice one thing we obtained flawed, have information that provides to this, or have a narrative you would like us to look into, write to us at [email protected].
Data: IPinfo’s Internet scans of IPv4 addresses, October 6–7, 2026, and 18 weekly scans from March 30 to October 6, 2026. Counts are addresses and a minimal.