Everybody’s dashing you towards passkeys, however here is the one factor no one mentions earlier than you delete your passwords
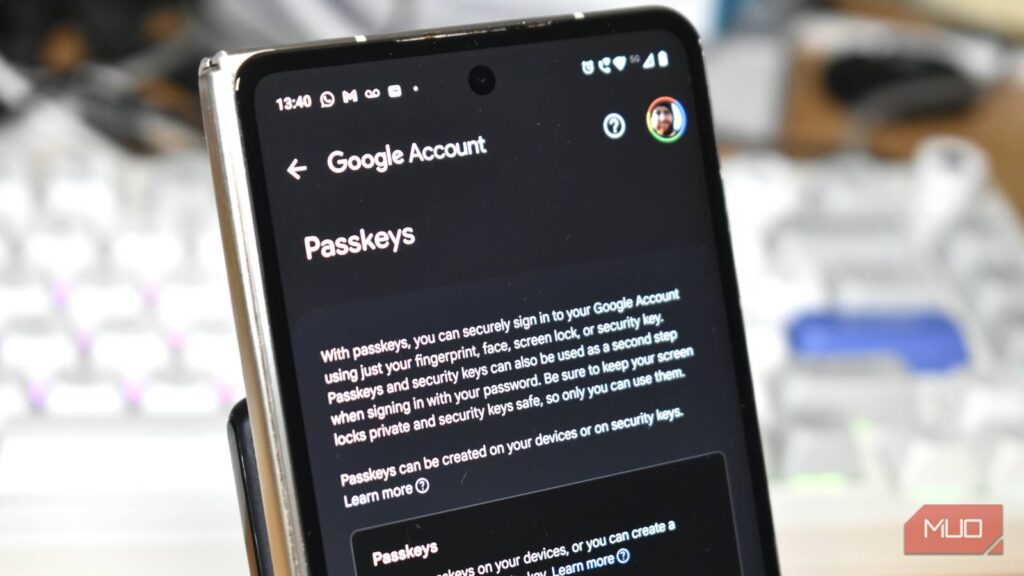
The tech business would very very similar to passwords to vanish. Google, Apple, Microsoft, and a rising variety of web sites now steer folks towards passkeys because the cleaner, safer solution to sign up, and the safety case is robust. Passkeys resist phishing, don’t go away attackers with a reusable secret if a website’s credential database is breached, and spare you from inventing one more remix of the identical password you’ve carried round since school.
I’m blissful to make use of them, however including a passkey and eliminating your password are two totally different choices. One offers you a stronger means into the account, whereas the opposite removes a fallback you should still want when your traditional gadgets aren’t round. Before I make that second transfer, I need to know precisely what’s ready on the opposite aspect if I ever get locked out.
Passkeys repair most of what makes passwords horrible
The password had a very good run, type of
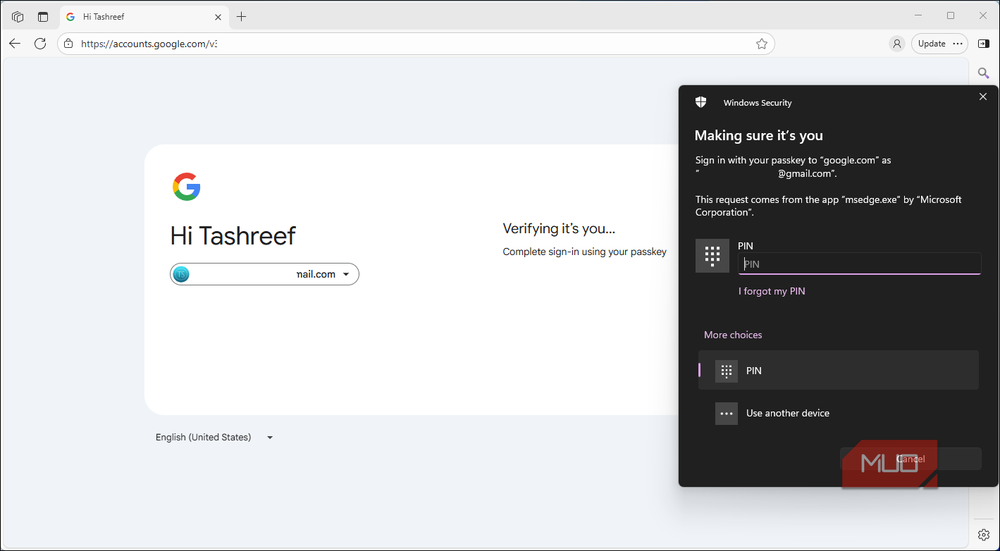
A password is a shared secret. You realize it, the web site shops sufficient data to confirm it, and each login asks you to show you already know it once more. That setup has given phishing kits, credential stuffing, password reuse, and database leaks loads of alternatives to trigger hassle.
Passkeys work differently by utilizing public-key cryptography. The web site shops a public key, whereas the matching personal key stays below your machine’s or credential supervisor’s management. When you sign up, your machine indicators a cryptographic problem and proves it has the best credential with out ever handing the personal key to the web site. That additionally shuts down one among phishing’s favourite methods. A faux login web page can’t merely persuade you to kind your passkey into the incorrect website as a result of the credential is tied to the reputable area.
Synced passkeys may also journey with you throughout gadgets by companies corresponding to iCloud Keychain, Google Password Manager, and third-party password managers. The credential supplier protects the underlying key materials, so it isn’t sitting round as a readable secret in some cloud folder ready to be copied.
That’s why shedding a cellphone by itself often isn’t the catastrophe folks image. If my passkeys are syncing correctly, I can change the cellphone, regain entry to the service managing these credentials, and restore them.
The uglier situation begins whenever you lose entry to each the machine and the service you’d usually depend on to get well these credentials.
Recovery will get sophisticated when all the pieces is determined by the identical account
Your backup plan wants a backup plan
Going passwordless places extra accountability on no matter system holds your passkeys. For many individuals, which means their Apple Account, Google Account, Microsoft account, or password supervisor turns into one of the vital essential components of their complete authentication setup. If a password supervisor goes to hold that a lot accountability, its security settings deserve a closer look too.
Apple, for instance, can sync passkeys by iCloud Keychain and affords a number of account restoration choices. Google helps restoration data, backup codes, different signed-in gadgets, safety keys, and extra passkeys. Microsoft’s passwordless accounts can depend on Windows Hello, Authenticator, safety keys, electronic mail codes, and different verification strategies.
That offers you loads of fallback choices should you’ve set them up prematurely. The hassle begins when a number of of these supposedly separate restoration paths depend upon the identical machine. Imagine your passkeys are saved in your cellphone, verification texts go to the SIM inside that cellphone, and your restoration electronic mail is best to achieve from the identical machine. Technically, you’ll have a number of restoration strategies configured, but one stolen machine can wipe out most of your entry in a single shot.
Two restoration strategies don’t offer you a lot redundancy if shedding one machine takes each with it. Device-bound passkeys make that particularly straightforward to see. A passkey saved solely on a selected laptop computer or {hardware} safety key gained’t reappear elsewhere after that {hardware} is misplaced or wiped. Account restoration can nonetheless work should you registered one other credential beforehand or the service affords one other solution to show who you might be.
The service itself additionally decides how account restoration works. Passkey requirements deal with authentication, whereas Amazon, PayPal, your financial institution, your electronic mail supplier, and each different service can set their very own guidelines for what occurs after you’ve misplaced each usable credential.
That’s the restoration web page I need to learn earlier than clicking take away password, not after I’m already locked out.
I will not delete a password till I’ve changed what it was doing
Before you burn the bridge, you must test the lifeboats

The best solution to plan for a passwordless account is to imagine that one among your gadgets will ultimately fail on the worst attainable second. Phones get stolen, laptops get wiped, and {hardware} safety keys have an uncanny means to fade into whichever drawer you have been completely certain you’d bear in mind later.
For any account you actually care about, you need at the least one restoration path that survives that form of failure. That would possibly imply registering passkeys on a number of gadgets you management, keeping a spare hardware security key someplace protected, storing restoration codes offline, or sustaining a restoration electronic mail account you possibly can nonetheless attain independently. The precise combine will differ by service, however you need these choices unfold out sufficient that one misplaced machine doesn’t take the entire restoration chain with it.
You must also test how transportable your passkeys are earlier than committing too closely to at least one credential supervisor. Portability has improved lots, and you can now move passkeys between password managers as Apple, Google, password-manager builders, and FIDO’s credential-exchange work begin breaking down among the outdated ecosystem boundaries. Support nonetheless varies between platforms and password managers, so confirm what your setup can truly export and import as a substitute of assuming migration might be painless later.
Keeping the password round for some time may also make sense in the course of the transition. An extended, distinctive password saved in a password supervisor offers you one other means again into the account whilst you arrange and take a look at the alternate options. You shouldn’t hold it perpetually as a pure emergency fallback, although. An energetic password continues to be a credential an attacker can phish, steal, or use to get into the account.
Once you might have a number of impartial passkeys and restoration strategies you belief, eradicating the password can shut off that weaker login route with out leaving you depending on a single machine.
Passwordless should not imply recovery-less
Going absolutely passwordless comes all the way down to what you’ll depend on when your traditional login setup isn’t obtainable. If you already know the way you’d get well the account with out that password, eradicating it is smart. If you don’t, there’s nothing incorrect with leaving an extended, distinctive password in your vault till the remainder of your restoration setup is prepared.