These 6 errors can flip Pi-hole into the least safe a part of your property community
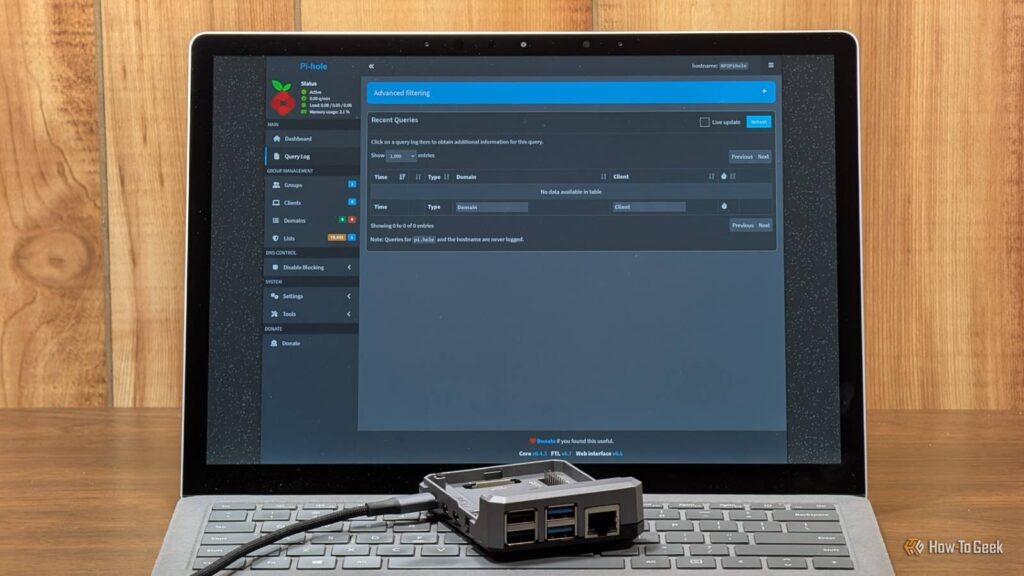
Pi-hole is considered one of my favourite providers that solves an on a regular basis downside with out requiring costly {hardware}. Install it on a Raspberry Pi, configure your units to make use of it for DNS, and you may block undesirable domains whereas monitoring DNS exercise throughout your community.
However, Pi-hole additionally handles community requests and offers an administrative interface that may expose quite a lot of delicate data. A couple of careless configuration decisions can flip this handy service right into a safety legal responsibility. I believe the largest hazard is assuming {that a} machine devoted to blocking advertisements doesn’t want the identical safety as a NAS, firewall, or server. Here are six errors that may put your property community in danger.
Port forwarding the admin dashboard to the web
Keep the administration interface personal
Pi-hole’s net dashboard can show DNS question historical past, consumer units, blocking statistics, and different details about your community. Depending in your configuration and question retention settings, somebody who beneficial properties entry may find out about your shopping habits and the providers your units use.
Forwarding the dashboard’s HTTP or HTTPS port by your router exposes it to internet-based assaults. A powerful password helps, but it surely can’t shield in opposition to each software program vulnerability or authentication bypass.
I perceive the temptation to verify Pi-hole whereas touring, particularly when a web site refuses to load, and you watched a blocked area. However, exposing the dashboard is pointless when you possibly can entry it by a VPN. WireGuard and Tailscale allow you to connect with your property community remotely and entry Pi-hole by a non-public connection. This offers you distant administration with out making the dashboard publicly accessible.
Setting DNS to “Permit all origins”
Do not unintentionally create an open resolver
Pi-hole wants to simply accept DNS requests from the units it serves. The hazard arises whenever you configure it to simply accept requests from arbitrary sources and expose its DNS service to the web. Pi-hole’s Permit all origins setting permits queries no matter their origin. Combined with public entry to port 53, this could create an open resolver that attackers abuse for DNS amplification attacks.
In these assaults, an attacker sends DNS requests utilizing a sufferer’s spoofed IP deal with. The resolver sends its responses to the sufferer, doubtlessly producing significantly extra site visitors than the attacker initially transmitted. Your Pi-hole may develop into a part of a distributed denial-of-service assault with out you realizing what is occurring.
For a typical residence set up, configure Pi-hole to simply accept requests solely from the networks it must serve. Use firewall guidelines to limit entry to port 53, and confirm that your router doesn’t expose the resolver to the general public web. If shoppers on a number of subnets want DNS entry, explicitly enable these networks fairly than opening the service to everybody.
Leaving the admin password clean
Secure the dashboard earlier than counting on it

Pi-hole can run with out an administrator password. That could also be handy on a trusted community, but it surely leaves the interface with out an essential layer of safety. This is particularly regarding as a result of Pi-hole has skilled vulnerabilities involving its configuration API. In 2026, a newline-injection vulnerability affecting FTL allowed an attacker with community entry to execute arbitrary instructions on sure installations with out an administrator password.
A compromised Pi-hole host may give an attacker management over the service and doubtlessly present entry to different assets reachable from that machine. Set a robust administrator password and limit entry to the dashboard. You can configure the password by Pi-hole’s command-line interface, utilizing the directions acceptable to your put in model.
Ignoring software program updates
Install safety fixes earlier than attackers exploit identified vulnerabilities

Pi-hole consists of a number of parts, together with its core utility, net interface, and FTL engine. Updates can deal with safety vulnerabilities in any of those parts. The 2026 FTL releases illustrate why upkeep issues. Versions 6.6 and 6.6.1 addressed configuration-injection vulnerabilities that might result in arbitrary command execution underneath affected circumstances.
Running an outdated model leaves your set up uncovered to issues that builders have already fastened. Publicly documented vulnerabilities may assist attackers determine unpatched methods. Check for updates repeatedly and observe the official improve directions. For a typical set up, pihole -up checks for and installs accessible updates. If you run Pi-hole in Docker, replace the container picture by your traditional deployment course of.
Back up your configuration earlier than important adjustments, and confirm that DNS decision works after updating. I’ve seen how simple it’s to neglect about providers that run quietly within the background. Pi-hole does not want every day consideration, however do not depart it unmaintained simply because the question counter retains transferring.
Assuming two-factor authentication makes you invincible
Protect the API as fastidiously because the login web page

Two-factor authentication provides safety by requiring a second verification step alongside your password. Pi-hole helps two-factor authentication since v6, but it surely can’t forestall each kind of assault. Vulnerabilities in API authorization or configuration dealing with can undermine protections supplied by the login course of. Pi-hole’s safety fixes show why retaining the applying patched stays vital even when extra authentication is enabled.
Pay explicit consideration to utility passwords. These credentials enable suitable functions to entry Pi-hole’s API, and their efficient privileges rely on the API permissions and implementation. A compromised integration can create dangers that aren’t instantly apparent from the dashboard.
Create utility passwords solely when vital, retailer them securely, and revoke credentials you now not use. Review which functions can entry Pi-hole, particularly in the event you join monitoring dashboards or automation instruments. I imagine two-factor authentication is value enabling, but it surely ought to complement software program updates and entry restrictions fairly than exchange them.
Running Pi-hole with out community segmentation
Limit what an attacker can attain from a compromised host

Pi-hole usually shares a community with private computer systems, NAS units, good TVs, and different gear. If an attacker compromises the Pi-hole host, unrestricted entry to that community may assist them uncover extra targets. For instance, an attacker would possibly scan for uncovered administration interfaces, examine weak providers, or try and entry community storage. The extent of the harm relies on the attacker’s privileges and the protections already in place.
Network segmentation limits these alternatives. You may place transport systems providers on a dedicated VLAN and configure firewall guidelines that enable the DNS site visitors shoppers want whereas proscribing pointless connections to delicate methods. If your router or switches don’t help VLANs, use the firewall controls accessible to you. Restrict administration interfaces, enable solely vital site visitors between units, and keep away from giving each machine unrestricted entry to all the LAN.
Segmentation requires some planning, notably if Pi-hole additionally offers DHCP or serves a number of subnets. Document which units want entry earlier than altering firewall guidelines, and take a look at DNS decision after making changes. For a homelab containing a NAS, digital machines, and self-hosted functions, I believe proscribing pointless community entry is effectively definitely worth the effort. One compromised service shouldn’t robotically give an attacker a transparent path to every part else.
Keep Pi-hole safe with just a few sensible safeguards
Pi-hole doesn’t want an elaborate enterprise safety setup, but it surely does want wise configuration. Keep its dashboard personal, limit DNS entry to trusted networks, use robust credentials, and set up safety updates promptly. After all, Pi-hole is meant that will help you management your community. Leaving its administrative interface or DNS resolver uncovered can hand that management to another person.