I finished utilizing SMS two-factor authentication after realizing how simply it will get intercepted
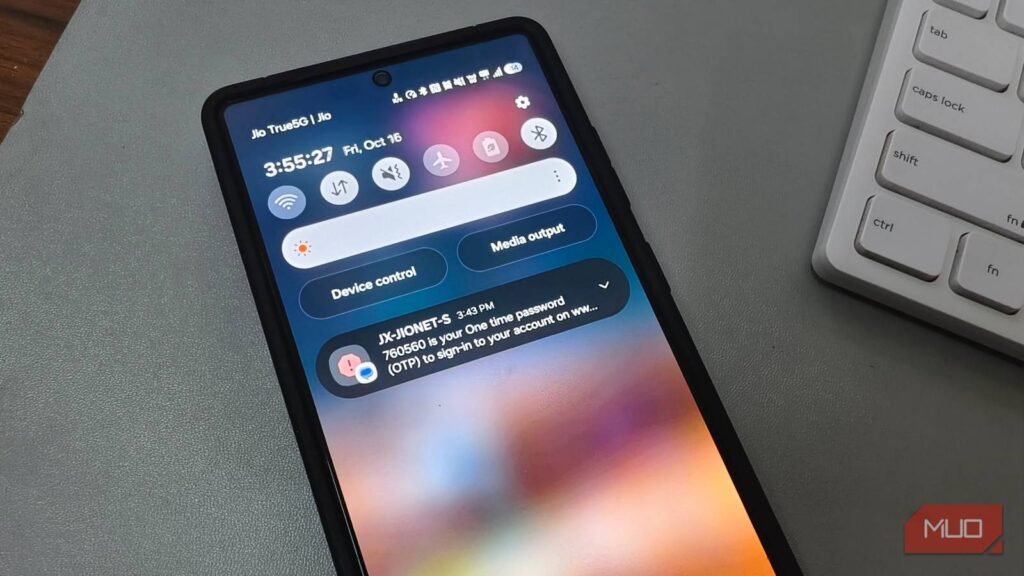
Right now, probably the most delicate accounts you personal most likely rely on a safety instrument that was by no means designed to guard you. We give our cell numbers to banks, password vaults, and e mail suppliers, trusting that so long as the cellphone is in our hand, the account is protected. For years, each time a six-digit code buzzed onto my lock display screen, I took it as proof that two-factor authentication was doing its job. Then I began tracing the route that code really travels after a service sends it, and the trail it takes earlier than it ever reaches my cellphone.
Your textual content message travels by means of a damaged system
SS7 routes your login codes with zero authentication

When you log in someplace and a six-digit code arrives by textual content, that quantity doesn’t journey by means of an encrypted channel. Your provider routes it throughout Signaling System No. 7, a protocol that telecom networks have used because the early Nineteen Eighties to deal with calls and textual content messages globally. SS7 was designed when solely a handful of state-backed operators touched the community, so the engineers who constructed it by no means added authentication. Every command the system receives is handled as official, no questions requested.
That design made sense many years in the past, however entry to SS7 has unfold far past these unique operators. Smaller carriers, third-party aggregators, and cross-border routing corporations all have entry now. An attacker with that entry can submit a routing request that tips telecom switches into treating your cellphone as if it have been on a overseas community. Your incoming texts, together with any verification codes, quietly reroute to a unique gadget, and your cellphone by no means exhibits a missed message.
This flaw turned actual in 2017, when attackers focused German financial institution prospects on the O2 community. They had already stolen banking credentials by means of malware on compromised computer systems, and when the banks despatched SMS authorization codes, SS7 instructions intercepted them mid-delivery. Account balances have been emptied earlier than anybody seen. Discovering that breach changed my mind about SMS verification, as a result of nothing I do on my finish issues when the transport systems itself treats each operator as reliable.
SIM swapping turns your quantity towards you
One cellphone name can reroute all of your verification codes
SS7 exploitation calls for entry to telecom transport systems, which limits who can pull it off. SIM swapping has no such barrier. In a typical SIM swap scam, somebody calls your cell provider, pretends to be you, and convinces a consultant to switch your quantity to a brand new SIM card. Once the swap goes by means of, each name and textual content meant for you lands on the attacker’s gadget, together with each SMS verification code tied to your accounts.
A 2020 Princeton University examine revealed simply how simple that is. Researchers examined fraudulent SIM swap makes an attempt at 5 U.S. pay as you go carriers and located an 80% success fee. Attackers bypassed safety questions by convincing employees to override verification insurance policies. In 2024, T-Mobile and Verizon workers obtained unsolicited textual content messages providing $300 for every accomplished swap.
That form of entry scales quick as soon as the tactic will get out. In the UK, SIM swap fraud surged 1,055% throughout 2024, leaping from 289 reported instances to just about 3,000 in a single 12 months. In Australia, 90% of SIM swap victims had no thought something had occurred till their cellphone dropped to SOS-only mode. T-Mobile paid $33 million in a personal arbitration after a single SIM swap value a buyer over 1,500 Bitcoin. The FCC adopted guidelines in late 2023 requiring carriers to strengthen their verification, however the wi-fi business pushed again and the compliance deadline was waived earlier than it ever took impact.
What I really use as an alternative of SMS codes
Authenticator apps and {hardware} keys maintain codes offline

Switching away from SMS verification turned out to be the straightforward half. Most providers that supply text-based codes additionally assist dedicated authenticator apps. You scan a QR code throughout setup, and the app shops a secret key domestically in your gadget. From that time, it generates a recent six-digit code each thirty seconds utilizing nothing however that saved key and your cellphone’s clock, so the code by no means leaves your gadget.

For accounts the place the stakes are highest, I added a physical hardware security key. A YubiKey plugs right into a USB port or faucets towards your cellphone over NFC, and the whole authentication occurs by means of a cryptographic examine tied to the particular web site area. A phishing web page on a lookalike URL will get no response from the important thing in any respect. It prices round $30 for a primary mannequin, and as soon as it’s registered, logging in means plugging in and tapping a button.
I began with e mail and banking, then labored by means of cloud storage, social media, and anything that also had SMS because the default. Every service I switched was one fewer account relying on a textual content message to maintain it protected.
SMS is a alternative, not a requirement
The greatest threat with SMS verification isn’t that higher choices don’t exist. It’s that the default by no means asks you to think about them. Carriers, platforms, and login screens nonetheless deal with a textual content message like a safe channel, and until you go on the lookout for the choice, nothing within the course of tells you in any other case.