I gave my sensible dwelling its personal DNS and eventually stopped my privateness settings from breaking it
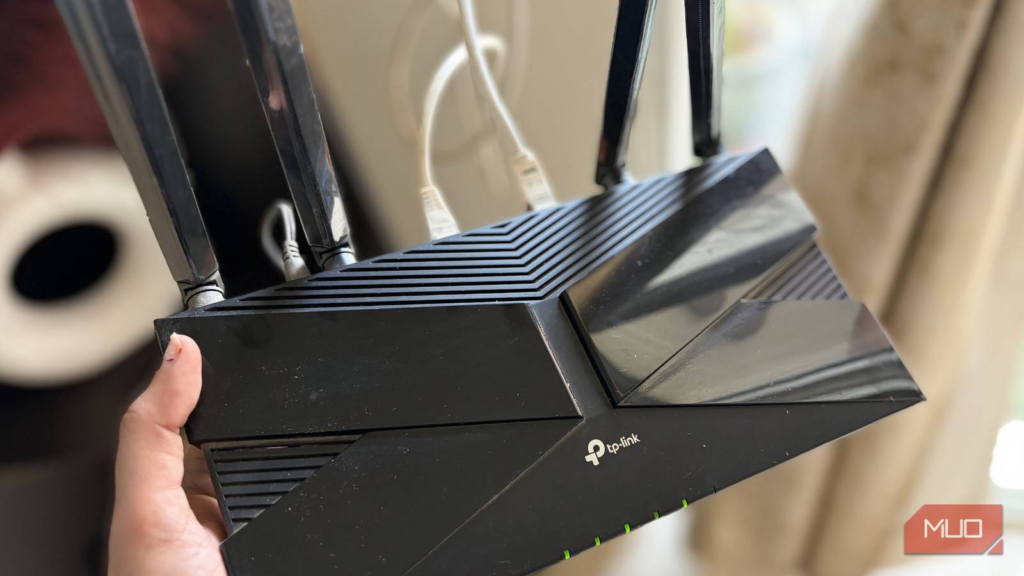
I’ve a network-wide privacy setup for my dwelling community that works superbly till it does not. Pi-hole blocked trackers on my laptops and telephones, however the identical aggressive lists periodically break sensible TVs, delay digital camera notifications, or go away a cloud-dependent bulb hanging off the web.
This left me in a loop of permitting one mysterious hostname, testing once more, and repeating till the machine got here again on-line. So I made a decision to offer my smart-home community its personal DNS coverage, and the fixed tug-of-war disappeared in a single day.
Pi-hole blocks the whole lot, together with your sensible bulb’s will to dwell
Your cellphone can present an error, your bulb simply silently provides up
The downside wasn’t DNS blocking itself. DNS-level filters are wonderful for units that can’t run browser extensions or privateness apps, as a resolver can refuse to return an deal with for a monitoring or malicious area, stopping the connection earlier than it begins. Pi-hole and AdGuard Home apply this safety throughout a community with out requiring shopper software program, which makes them relatively helpful in the case of IoT units.
That mentioned, you may run into issues should you use one blanket coverage for each machine. My cellphone can tolerate strict blocklists as a result of I can see an error, examine the question log, and work round it. A wise bulb, nonetheless, can’t clarify that its login endpoint, telemetry host, and command service sit behind associated domains. If any of these domains is blocked, it simply stops responding. Relaxing your filters for the whole lot will get the machine again on-line, but it surely weakens safety for units that benefited from the stronger blocklists within the first place.
Your sensible dwelling will get its personal DNS lane, and the chaos stops
Different units, completely different insurance policies, similar {hardware} should you’re lazy

My answer was to deal with smart-home units as a category of their very own. They already dwell on an remoted 2.4 GHz community, so I assigned that community a dedicated DNS resolver. A separate bodily server is elective right here; one other Pi-hole or AdGuard Home container, VM, or occasion on present {hardware} works simply as nicely. The distinction is the coverage, not the service working it.
The router’s DHCP service advertises the IoT resolver solely to purchasers on that particular community, whereas my trusted community continues utilizing the stricter resolver. Pi-hole can even assign purchasers to teams with completely different lists and guidelines, so the identical result’s potential with one occasion if the resolver can reliably establish every shopper. AdGuard Home additionally helps client-specific settings and domain-specific upstream resolvers.
This separation provides you a sane default. Computers and telephones hold aggressive advert, malware, and monitoring safety whereas sensible dwelling units get a smaller, security-focused blocklist along with specific blocks for examined telemetry domains that do not break my units. If a vendor endpoint is required for setup, authentication, notifications, or firmware checks, I permit it solely on the IoT coverage. I now not should punch a network-wide gap to revive one temperamental sensible plug.
Query logs lastly matter once they’re solely about your devices
Find the one area your sensible plug wants, then cease guessing

The largest trouble of this strategy is that there isn’t any common blocklist you may obtain off the web and use right here. The domains you find yourself blocking can be particular to the sensible units you will have round the home, so you are going to should dig by means of the logs. The upside is that as a substitute of looking out by means of hundreds of queries from browsers, apps, and working techniques, you may see exactly what your smart devices request across the time a characteristic failed. Then, you may quickly disable filtering for that shopper, reproduce the issue, evaluate the outcomes, and permit solely the minimal crucial area.
That does not make each question malicious or show what knowledge a tool sends. DNS reveals the hostnames a tool tries to succeed in, not the contents of an encrypted connection. Still, the smaller dataset makes patterns apparent, reminiscent of repeated telemetry lookups, surprising third-party companies, or a tool that retains contacting the cloud even while you management it domestically. DNS filtering could be a helpful management level, but it surely enhances LAN guidelines and outbound firewall restrictions as a substitute of merely changing them.
Names beat numbers: ha.dwelling.arpa as a substitute of 192.168.one thing
RFC 8375 gave your LAN a suffix, and .native can keep out of it

A facet advantage of working a devoted smart-home resolver is that I additionally made it authoritative for inside names. This implies that as a substitute of typing an IP deal with and port quantity each time I needed to entry a service, I can now use URLs like ha.dwelling.arpa for Home Assistant, mqtt.dwelling.arpa for my MQTT dealer, and so forth. Both Pi-hole and AdGuard Home help native data or DNS rewrites that map a hostname to a LAN deal with.
I used dwelling.arpa on function. RFC 8375 reserves it for non-unique naming inside residential networks and says these queries ought to be answered domestically relatively than forwarded onto the web. This additionally saved me the trouble of inventing a suffix and did not overload .native, which belongs to multicast DNS and is meant to be resolved on the native hyperlink utilizing mDNS.
Internal naming additionally eliminated hard-coded IP addresses from dashboards, scripts, and Home Assistant integrations. If I transfer a service to a different host, I replace one DNS file as a substitute of scanning by means of configuration recordsdata. DNS rewrites can even present split-horizon conduct, the place the identical public hostname resolves to a personal deal with at dwelling and its public deal with elsewhere, a typical sample for Home Assistant setups.
Congratulations, you now run important development projects
Backups, a second resolver, and IoT units that ignore you anyway

The largest downside with this strategy is the truth that a devoted resolver rapidly turns into development projects you need to keep. It wants a steady deal with, backups, monitored storage, and ideally a second resolver. Advertising a public resolver as secondary will not be a clear failover, as purchasers could use both server and find yourself bypassing native filtering or inside names. Both marketed addresses ought to subsequently implement the identical native coverage.
Some IoT merchandise additionally use hard-coded resolvers or encrypted DNS. I ended up dealing with atypical exterior DNS with firewall guidelines that redirect or block port 53 from the IoT LAN, however encrypted DNS requires extra intentional controls and might be tough to separate from common HTTPS site visitors. IPv6 additionally wants consideration, since an missed router commercial can hand units a resolver that bypasses the IPv4 setup.
Privacy works higher when it is not one-size-fits-nobody
A looser smart-home coverage made the entire community safer, one way or the other
In the tip, the largest enchancment is not blocking extra domains, it was accepting that privateness controls ought to match the machine. My sensible dwelling DNS is deliberately much less aggressive, but the general community is extra personal as a result of I now not weaken the principle coverage each time an equipment breaks. At the identical time, native service names make setup and entry simpler to maneuver, doc, and restore.
DNS will not all of the sudden make shady units reliable, but it surely does offer you clearer boundaries, a centered log, and a managed place to resolve what every machine could resolve. That small architectural change lastly permits reliability and privateness to coexist as a substitute of taking turns breaking one another.