Your sensible gadgets are quietly ignoring your Pi-hole, right here’s cease them
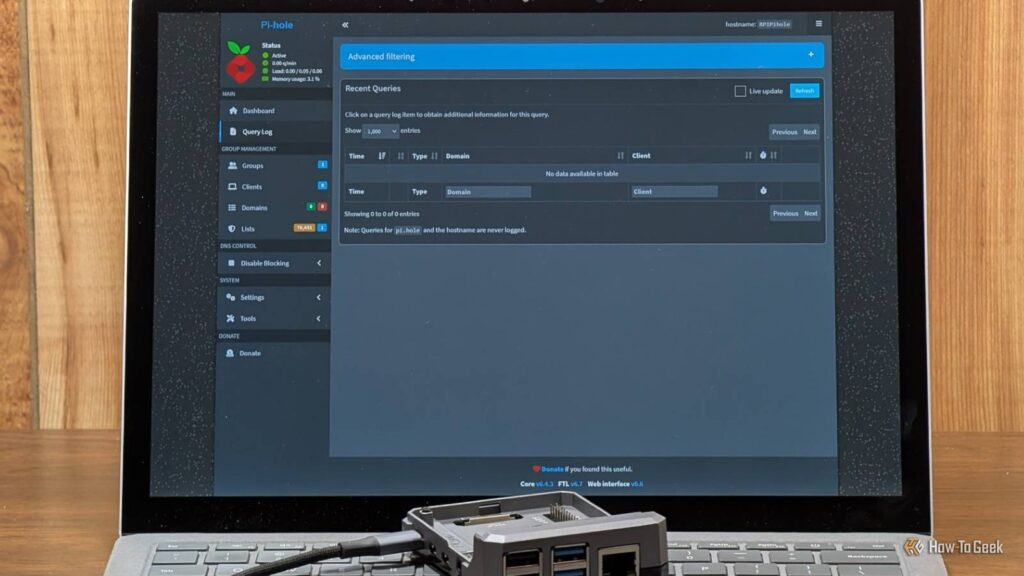
If you take a look at your Pi-hole dashboard after just a few weeks of use you may see hundreds, if not tens of hundreds, of blocked queries. Yet, regardless of your greatest makes an attempt, there are nonetheless adverts enjoying in your TV.
The drawback in all probability is not with the Pi-hole itself or something you probably did—it’s in all probability the TV. Unfortunately, an growing variety of gadgets and providers will bypass a Pi-hole as if it weren’t even there.
This is how they do it, and how one can repair it.
What Pi-hole can and might’t see
It can solely filter the DNS queries which are despatched to it
A Pi-hole works by sitting between the gadgets in your community and an out of doors DNS server. From that place, it might probably selectively block DNS lookup requests. When your PC tries to retrieve the IP tackle of a web site on the Pi-hole’s block listing, the lookup fails to undergo.
Most gadgets and apps will defer to your router’s DHCP settings to specify their DNS server, which is why the Pi-hole works in any respect. The snag is that apps, providers, and gadgets do not have to respect what your router tells them.
A Pi-hole may fail to filter adverts and trackers that come from the identical area because the content material you wish to view. Blocking an advert in that scenario would essentially block the video you are attempting to stream too.
Why gadgets bypass the router and Pi-hole utterly
Hard-coded and encrypted DNS skip your resolver fully
Unfortunately, many gadgets are designed to bypass your native settings to make sure they keep linked to the producer’s servers. Smart TVs, streaming sticks, and sensible audio system typically have hard-coded DNS settings, which suggests they question a public DNS server like 8.8.8.8 no matter what your router says.
Encrypted DNS presents one other problem. Browsers and an growing variety of different apps use DNS over HTTPs (or one other encrypted commonplace), which hides the lookup knowledge inside HTTPS site visitors which travels by means of port 443. Android’s private DNS feature makes use of one thing comparable referred to as DNS over TLS (port 853) or DNS over HTTPs.
That signifies that the exact same mechanism that protects your DNS lookup requests from the prying eyes of your ISP (and others) prevents your router from recognizing them and forcing them by means of the Pi-hole.
If your router has logs, search for outbound site visitors on ports 53 (common DNS) and 853 (DoT) that is not coming from the Pi-hole.
Blocking the site visitors Pi-hole cannot cease
You have to make use of the router

There are just a few various things it’s good to do to plug up the leaks.
First, configure your router at hand out the Pi-hole because the solely DNS server for each IPv4 and IPv6. There is an opportunity some site visitors is slipping by means of a secondary DNS or a separate IPv6 DNS.
Second, some routers let you arrange a rule that redirects all outbound site visitors on port 53 to the Pi-hole first. That forces hard-coded however unencrypted DNS requests by means of the Pi-hole, which can be related to many sensible gadgets, together with many TVs and some sensible fridges I’ve encountered. Just be sure you enable the Pi-hole itself by means of, or nothing will work.
You may additionally utterly block outbound site visitors on port 853. That successfully prevents gadgets from utilizing DNS over TLS to slide previous your Pi-hole. It will even imply that you just functionally lose DoT in your community too, except you specifically configure the Pi-hole (with Unbound) to make use of DoT after it has an opportunity to filter the whole lot.
Unfortunately, DNS over HTTPS (DoH) is extra sophisticated to cease. To catch these requests, it’s good to use your router to dam the IP addresses of DNS servers that assist DNS over HTTPs. Any machine hard-coded to make use of DoH will then both fallback to common DNS or be blocked utterly. There are DoH IP blocklists accessible on the net, so you do not have to assemble that listing by hand.
Your router could not allow you to
Most shopper routers lack the mandatory controls

Unfortunately, for those who’re utilizing a normal ISP router and even many shopper routers, you may in all probability discover you have no choices. You’ll have the ability to change your DNS server to allow the Pi-hole, however your router in all probability does not assist the form of NAT redirects or firewall guidelines that it’s good to deal with the instances the Pi-hole does not catch.
It is not that the router is not bodily succesful—all routers are—however the producer has chosen to not make the required settings accessible to you within the software program.
There are just a few choices. You may flash third-party router software, like OpenWrt, onto your router if it helps it. You may additionally bodily assemble your personal router and use specialised software program like OPNsense or pfSense, which provide you with complete management over how your community operates.
A DIY wired router is a neater challenge than it appears like. You simply want a PC with two quick Ethernet ports, OPNsense, and some hours to muddle by means of the first-time setup pains.
If none of these are an choice, you simply need to do what you’ll be able to on a per-device foundation. In the case of a wise fridge, that in all probability simply means disconnecting it from the Wi-Fi.
The Pi-hole is nice, but it surely solely works with cooperative gadgets
A Pi-hole is nice, and everybody ought to have one if just for the power to dam particular malicious domains and regulate their community. However, it’s restricted by the truth that gadgets in your community aren’t required to make use of it.
Even with the very best Pi-hole setup within the globe, you will not cease first-party adverts or each single DoH shopper.