I desire OpenWrt to OPNsense, however this old-school Linux router matches most networks higher
When my community wants a brand new router, I often attain for OpenWRT earlier than OPNsense. They’re each extraordinarily capable edge routers, particularly when deployed as a VM. However, as soon as I begin stacking interfaces, VLANs, and guidelines, I discover myself needing to attract out the topology to recollect which networks can attain which others.
It’s simply an excessive amount of complexity when all I would like is a lab router.
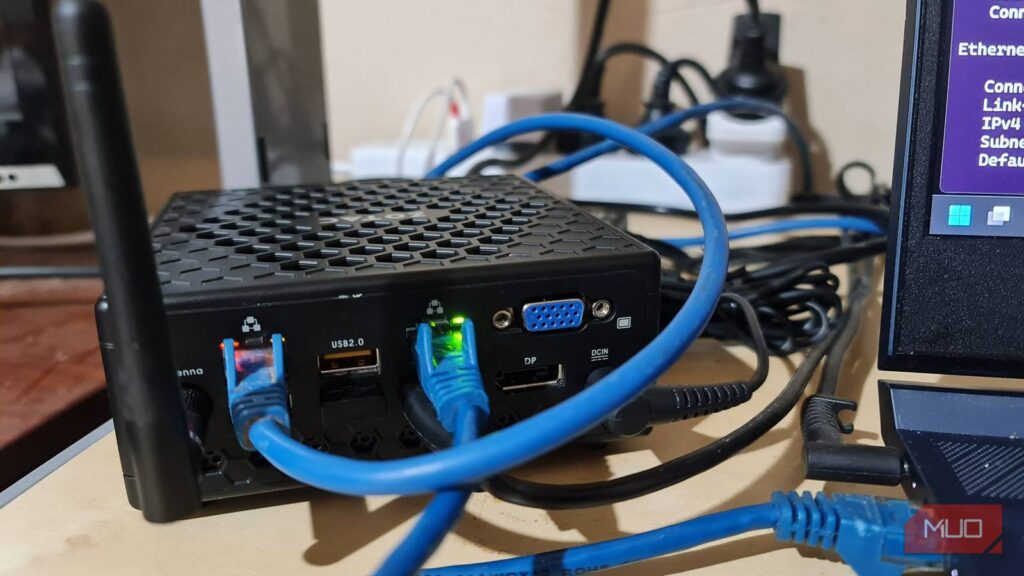
IPFire’s color-coded RED, GREEN, ORANGE, and BLUE zones provide a less complicated strategy to image these boundaries. My spare ZOTAC mini PC had two Ethernet ports and an Intel Wi-Fi card, giving every community its personal bodily interface and making the entire structure far simpler to work with.
The ZOTAC gave me a tangible community boundary
Two Ethernet ports gave my experiments their very own nook of the community
My little ZOTAC Mini PC was sitting round amassing mud after I attempted to make it into a hypervisor. With IPfire, it lastly had a job that suited its {hardware} and, let’s face it, pretty mediocre Celeron processor.
Its twin NICs, Intel Wi-Fi card, 8GB of RAM, and SSD gave me every little thing I wanted to show it right into a router equipment.
IPFire requested me to decide on a community structure throughout its preliminary setup, and I selected GREEN + RED. This is the place the colours actually began to click on for me. Each coloration comes with not solely a kind of community, however a selected job. This gave me a helpful community map earlier than I’d even written a single firewall rule.
|
Zone |
Purpose |
My setup |
|---|---|---|
|
RED |
Upstream community |
Existing edge router’s LAN |
|
GREEN |
Trusted wired community |
10.77.60.0/24 lab |
|
BLUE |
Separate wi-fi community |
10.77.60.0/24 lab |
|
ORANGE |
DMZ for uncovered servers |
Unused in my construct |
During setup, IPFire additionally asks which community interface I wish to assign to which coloration. It lists the out there adapters by their MAC addresses.
Looking on the again, I had a 50/50 probability the Network Interface Card (NIC) on the right-hand aspect could be the RED community, related to my LAN, and the remaining NIC could be the GREEN community. After a bit trial and error consisting of plugging my laptop computer into every port with a crossover cable, I found that, after all, I guessed fallacious.
I ended up with the RED community assigned to the left-hand NIC, and the GREEN community to the correct. I set RED to get its handle through DHCP from my edge router, like every gadget on my LAN. GREEN received the mounted handle of 10.77.50.1, and I enabled IPFire’s DHCP server at hand out lab addresses from 10.77.50.100 to 199.
The wired part of the lab was now alive, and either side had a transparent job. Eventually, I might add a BLUE wi-fi community, however first I wanted to isolate the lab community correctly.
My lab wasn’t remoted till I wrote the correct rule
The first ping take a look at discovered a route again into my house community

The laptop computer, related to GREEN, had an handle, DNS labored, and web sites loaded. Then I pinged a tool on my house LAN solely to find it answered again with a pleasant ICMP Echo Reply. As it seems, IPFire’s default firewall settings meant my experiments might nonetheless wander subsequent door.
The rationalization was simple. GREEN might ship site visitors by means of RED, and my house community sat on that upstream aspect. Giving the lab a different subnet wasn’t sufficient to maintain the site visitors away from the remainder of my community.
Luckily, IPFire makes creating firewall guidelines tremendous straightforward. I created a DROP rule that focused 192.168.1.0/24 throughout all protocols. Setting the supply to Standard networks → GREEN put the rule beneath Forward Firewall Access, the place site visitors passing by means of the router belonged. After saving and making use of the rule, I repeated my earlier assessments:
- The house community gadget stopped answering pings.
-
1.1.1.1nonetheless replied, displaying that public web entry hadn’t been damaged by the rule.
That was the boundary I wanted. The lab might use my web connection with out getting free entry to every little thing on the upstream community.
When creating IPFire firewall guidelines, select a community beneath Standard networks when filtering its shoppers. The annoyingly comparable “Firewall” choice refers to IPFire’s personal interface handle.

- OS
-
Standalone Linux-based firewall distribution
- Key highlights
-
Color-coded community zones, configurable firewall guidelines, site visitors graphs, and add-on packages
BLUE turned the spare Wi-Fi card right into a second lab
The entry level labored as soon as I ended trusting computerized channel choice

The ZOTAC’s Intel Wireless 3165 gave me a strategy to carry telephones and different wi-fi take a look at gadgets into the lab. First, I checked its capabilities to verify it supported access point mode:
iw checklist | grep -A 12 'Supported interface modes'The {hardware} supported not solely AP mode, however monitor and P2P consumer as effectively.
Back within the console setup, I modified the community sort to GREEN + RED + BLUE and assigned the wi-fi adapter to BLUE. I gave the BLUE interface the IP 10.77.60.1/24 and enabled DHCP for addresses from 10.77.60.100 to 199. I then put in the hostapd entry level add-on by means of IPFire’s package manager.
The new wi-fi configuration web page let me title the community IPFire-Lab-Blue, set the nation code, and decide the wi-fi mode: IEEE 802.11an/gn 20 MHz. I set the band to five GHz with an auto-selected channel, saved, and began the wi-fi entry level.

For about 10 superb seconds, the service reported RUNNING, then stopped earlier than my cellphone might even discover it. I needed to dive into the logs to search out the explanation why the AP saved getting disabled after beginning:
grep -iE 'hostapd|blue0|iwlwifi' /var/log/messages | tail -n 60The purpose for this failure turned out to be extremely attention-grabbing. The computerized channel choice had determined that the 5 GHz channel 52 was the perfect place to broadcast.
Channel 52 can also be utilized by some army, air site visitors management, and climate radar techniques. That means the AP should take one minute to verify for these earlier than broadcasting, generally known as Dynamic Frequency Selection (DFS).

That delay was inflicting hostapd to desert startup and cease the service from operating. Switching to 2.4 GHz with a fixed channel introduced the community up immediately. My cellphone related, and IPFire’s coloration mannequin had gained one other helpful boundary.
I opened precisely one door from BLUE to GREEN
An area dashboard loaded on my cellphone whereas the remainder of the wired lab stayed closed

My cellphone joined BLUE and was in a position to attain my native LAN. That route was closed for GREEN, however wi-fi shoppers wanted their very own guidelines. I added one other DROP rule concentrating on 192.168.1.0/24, this time with Standard networks → BLUE because the supply. After making use of, the sting router stopped answering pings, whereas outdoors web entry remained.
Next got here testing some extra outlined boundaries. I spun up a VM on my laptop computer and put in the Homarr dashboard through a Docker container. Since the VM’s community was in bridged mode, it acquired an IP handle 10.77.50.101 from the GREEN DHCP server.
The cellphone now couldn’t ping it, which was high quality, however I wished entry to the dashboard with out giving wi-fi gadgets entry to all the subnet.

I created an ACCEPT rule from BLUE to 10.77.50.101 and restricted entry to TCP vacation spot port 7575. Opening http://10.77.50.101 on the cellphone introduced up the dashboard’s login display, however making an attempt to ping the identical IP failed. Ping failed just because I’d allowed the dashboard’s TCP site visitors, and never ICMP.
I now had a helpful and focused association for testing. Wireless gadgets might attain a single service I designated by means of firewall guidelines, whereas the remainder of the house and GREEN LAN stayed off-limits.
I might see what the firewall was doing
Connection particulars and graphs are what make IPFire so good for testing

Once the boundaries labored, I wished to see what was truly crossing them. IPFire’s Connections web page is a strong approach of seeing the supply and vacation spot addresses of lively connections, together with geolocation.
I wished to check this performance, so I used an internet site that wouldn’t take the scenic route by means of a CDN — the University of Ghana’s web site at https://ug.edu.gh. The Ghanaian flag appeared in my Connections output, which gave me a helpful coverage take a look at.

I briefly blocked site visitors from the lab to all the nation through a geoblocking rule, and the web site timed out. I eliminated the rule afterward, having proved the conduct I wanted to check.
IPFire’s graphs additionally give me a broad view. Separate GREEN and BLUE site visitors charts let me have a look at and evaluate exercise on the wired and wi-fi networks. The firewall-hit graph additionally reveals each dropped or rejected packet over time, and {hardware} graphs keep watch over system temperatures and useful resource utilization.

These views assist me to examine particular assessments, and the graphs present all the encircling exercise. They additionally look unbelievable, which actually doesn’t harm.
IPFire earned its place regardless of the gotchas
OpenWrt’s nonetheless my favourite, however IPFire matches this bodily lab

IPFire makes networking easy, however it nonetheless comes with loads of set up and setup gotchas. Probably top-of-the-line (and ironic) examples of this was not with the ability to entry IPFire’s personal web site by means of the router.
www.ipfire.org returned SERVFAIL when the upstream edge router’s DNS resolver failed to finish DNSSEC and validate the area. Switching IPFire to 1.1.1.1 mounted that difficulty, however it’s nonetheless an annoying complexity in what ought to in any other case be a reasonably simple setup.
Still, the ZOTAC has now given me a wired lab, a separate wi-fi zone, particular exceptions between them, and very helpful information through graphs.
I’d nonetheless attain for OpenWRT once I want the flexibleness. For this field, although, IPFire’s colours gave each interface an outlined job and made the foundations far simpler to know. The setup took some persistence, however in the long run, I’ve a lab I perceive effectively sufficient to begin breaking issues in it.