I did every part to cover my shopping from my ISP, and it might nonetheless see most of the place I went

The massive concern with on-line privateness is that it is continually evolving, and the large tech corporations will at all times discover new methods to get into your information.
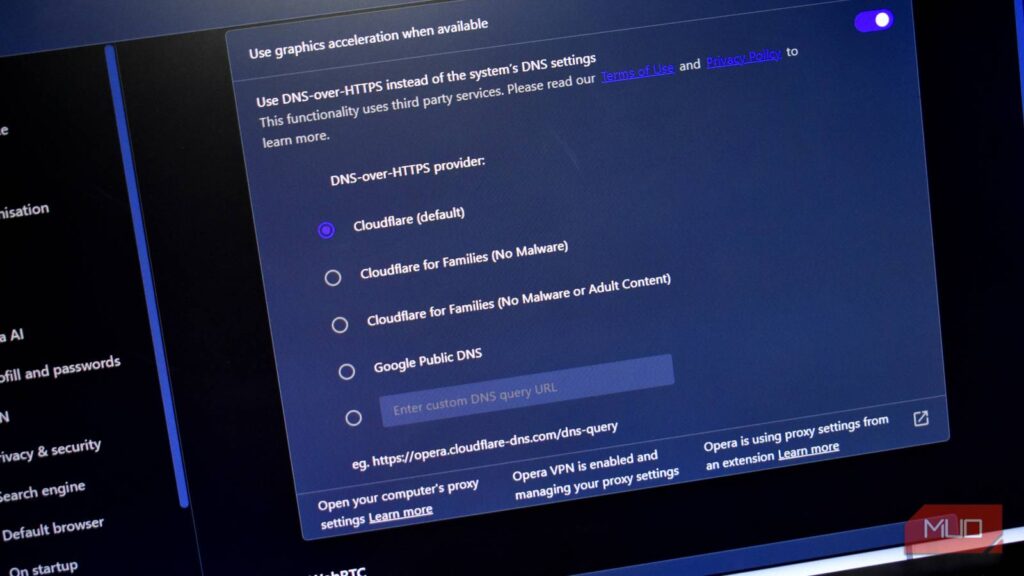
You can repair — or not less than, attempt to repair — lots of the issues from dwelling: toggling encrypted DNS to your complete dwelling, forcing HTTPS all over the place, locking down your browser configuration or utilizing a privacy-focused browser, and so forth, to spice up your privateness above and past most folk.
But even with all these toggles, switches, and privateness apps, one hole can nonetheless undermine all of it: your ISP.
What your ISP truly sees
It’s tough to flee its gaze
Every connection you make on-line is routed via your ISP in some unspecified time in the future. It’s what retains you linked to the web, and sure, your provider technically counts as an ISP, so that they’re included right here, too.
For all the privateness toggles and apps, there are nonetheless a number of bits of knowledge your ISP will nonetheless see.
For instance, chances are you’ll use an encrypted DNS supplier like Quad9 or Cloudflare, however the connection course of can nonetheless expose the Server Name Indication (SNI), and your IP deal with and the goal deal with can nonetheless be uncovered within the uncooked communication between your gadget and the web site, app, or service.
If you are utilizing unencrypted DNS, the entire lookup is shipped in plaintext, which implies your ISP can see every part you seek for and connect with.
Similarly, the TLS handshake may reveal details about you to your ISP. Even on a totally encrypted connection, the primary message your gadget sends names the positioning you are after (the SNI once more), and it usually travels in plaintext so the server is aware of the proper safety certificates to use.
The answer to this, Encrypted Client Hello, is already in your browser, however I’ll discuss this in additional element in a second.
Finally, the vacation spot IP. When you utilize the web in nearly any type, you are connecting to distant servers to entry the data held on them, and which means you are continually asking to hook up with a particular vacation spot IP. Unfortunately, even with encrypted DNS, web site fingerprinting remains to be doable, particularly throughout the ISP’s personal IP block.
As discovered within the 2023 paper Lightweight and Effective Website Fingerprinting over Encrypted DNS, “encrypted DoH [DNS over HTTPS] visitors may very well be exploited to determine web sites {that a} consumer has visited . . . Our mannequin and algorithm can precisely predict one out of 10,000 web sites with a 95% accuracy utilizing the primary 50 DoH packets. In the open-world setting with 100,000 web sites, our mannequin achieves an F1-score of 93%.”
That stated, shared IP addresses imply the positioning or service is usually hidden behind a single IP deal with pool, however your ISP can nonetheless decide your vacation spot IP more often than not.
The privateness and safety settings you could hold toggled
It’s not that it isn’t value doing

You ought to nonetheless hold your entire privateness toggles and settings switched on, thoughts. Just as a result of they are not good doesn’t suggest they are not value utilizing. If we continually strived for perfection, nothing would ever get achieved.
Encrypted DNS
That means switching on encrypted DNS system-wide is nicely value doing, as a result of it removes not less than a number of the information revealed to your ISP throughout the lookup and determination course of. You can change your DNS settings and toggle encrypted DNS on all major operating systems, and it solely takes a minute or two.
You might additionally take into account installing a custom DNS server to protect your entire network, or take into account switching your ISP’s DNS settings directly on your router.
Encrypted Client Hello
Encrypted Client Hello additionally helps to shut a few of that hole, too. While HTTPS is usually pointed to as a privateness function, and it undoubtedly has improved on-line privateness and safety, it isn’t with out points.
One of the core elements of web communication is the TLS handshake, which establishes the encrypted hyperlink between your gadget and the server. But as a part of that course of, the Client Hello message consists of the positioning’s hostname in part of the method known as the Server Name Indication (SNI) discipline.
That discipline has at all times traveled as plaintext, which means that even within the period of HTTPS, it is information that your ISP can see. Now, it is helpful information for the web site server, because it’s the way it identifies the certificates to return to your gadget earlier than encryption begins.
It’s exactly this little hole in safety that Encrypted Client Hello protects, beginning with the publication of RFC 9849 in March 2026.
Basically, ECH builds a second model of the handshake message and nearly makes use of it like a decoy. One encrypted message holds the true info, such because the hostname, whereas the opposite is shipped within the clear with a generic placeholder title as a substitute. The server unlocks the true model as soon as it arrives and carries on as regular, however your ISP solely ever sees the decoy.
ECH is now applied in most browsers, and there is not a toggle you may flip to show it on, however it’s helpful understanding that it is now being rolled out nearly all over the place to spice up your privateness.
HTTPS-Only modes
Despite the hole simply illustrated in HTTPS, it is completely value protecting switched on, and even to go so far as to pressure each website to make use of it.
The function has completely different names, relying in your browser, however the normal concept is similar: each connection will use HTTPS the place doable, and dangerous websites and connections might be blocked and rejected.
Enabling your browser’s HTTPS-only mode is likely one of the quickest methods to spice up your privateness.
The actual answer is to make use of a VPN for every part
There is at all times going to be some information leakage to your ISP, nearly it doesn’t matter what you do. That’s why, when you actually wish to cease your ISP and different third events from viewing what you are as much as on-line, a VPN is a core a part of the method.
When you utilize a VPN, your DNS, SNI, vacation spot IP, and just about every part else is scooped up and routed via the VPN’s encrypted tunnel, supplying you with an enormous privateness increase and obscuring your on-line actions out of your ISP.
Now, your ISP can nonetheless see some info. It is aware of that you simply’re utilizing a VPN, the quantity of knowledge you are sending and receiving, and your actual IP deal with. But something within the encrypted VPN tunnel is protected, which is why, when you actually wish to shield your information out of your ISP in any respect prices, a VPN like Mullvad is significant.