You in all probability don’t acknowledge half the processes operating on Windows, and that’s a safety drawback
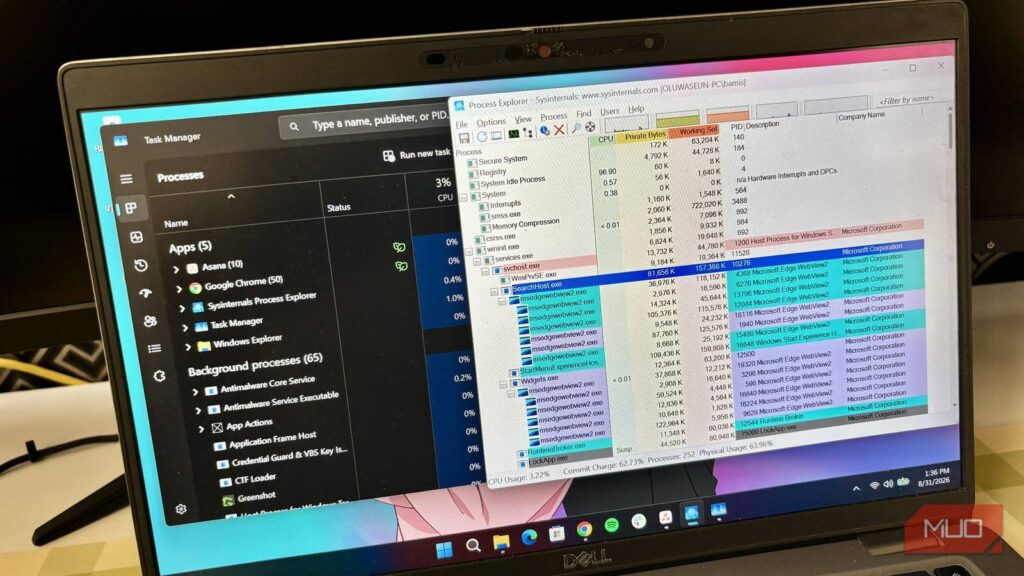

I’ve a behavior you may name paranoia: I’m going hunting through the Task Manager as soon as my pc’s fan begins spinning louder than regular with the goal of “catching the burglar mid-heist.” This behavior paid off final week, besides this time the “burglar” was a course of I’d by no means questioned earlier than.
Eventually, I noticed the larger drawback wasn’t that I did not acknowledge a course of. It was that I did not have a dependable method to inform whether or not it deserved my consideration.
One course of on my listing I genuinely could not clarify
Its title gave me nothing — the file beneath informed a special story
While I scrolled by Process Explorer, the road that caught my consideration was RuntimeBroker.exe, PID 18900. This course of used about 7.8MB of personal reminiscence. Alone, I could not have bothered, however once I noticed 4 further cases of the identical course of, I turned curious sufficient to research.
They have been all operating beneath completely different PIDs: 18900, 23036, 19616, 20936, and 7104, and so they consumed barely completely different quantities of reminiscence.
The title itself — “RuntimeBroker” — wasn’t giving me a lot to work with. In reality, at one level, I used to be satisfied this was the sort of factor a scammer would title a faux course of. It sounded each imprecise and official directly.
So I right-clicked on it and explored its properties. In the Properties window, I may see greater than the title gave away, together with the executable’s path and its digital-signature info.
It took just a few seconds for me to go from hunch to precise solutions. This modified how I work together with processes. I did not have to acknowledge each course of, however I wanted a method to study extra about them.
I turned on a second opinion
Checking a reminiscence VirusTotal already had
By wanting by the Company Name column of Process Explorer, I may see that it was signed by Microsoft Corporation. Also, the trail confirmed me that it was operating from System32. Those two particulars made a faux RuntimeBroker a lot much less doubtless, however I wasn’t able to accept “appears nice.”
So, I enabled an additional column. I navigated Options > VirusTotal.com > Check VirusTotal.com, then accepted the one-time phrases. In just a few seconds, that column populated.
What I favored was that Process Explorer first checked the file’s hash in opposition to VirusTotal quite than mechanically importing my copy of the executable. VirusTotal may return an present consequence if that hash was already in its database. If a file is not already recognized, Process Explorer also provides an option to submit it for analysis, so I wasn’t treating the mixing as a assure that recordsdata can by no means depart the PC.
The consequence for this particular course of was 0/76 on the time I checked it. When I clicked its VirusTotal entry, I used to be taken to a web page exhibiting “No safety distributors flagged this file as malicious.”
I had assumed that VirusTotal would truly run a stay virus scan, however this wasn’t the case. Instead, it queries a big, repeatedly up to date database to see whether or not that file has been seen earlier than and what distributors reported.
That quantity wasn’t the reply I assumed it was
It solely meant one thing as soon as I finished studying it alone

When I noticed the clear VirusTotal consequence, I used to be tempted to deal with it as the top of my investigation. A zero-detection consequence does not show {that a} file is protected. It can merely imply that not one of the taking part engines detected it as malicious, or that the file is just too new or uncommon for present signatures and detections to catch.
Also, seeing only one detection inside numerous engines does not essentially affirm that it is malware. A solitary detection will also be a false constructive.
Hence, VirusTotal alone wasn’t what settled issues for me. I drew conclusions by studying that column and making an allowance for every little thing that Process Explorer had already proven me. In the case of this particular file, I verified that it sat the place a real RuntimeBroker ought to sit and that its digital signature recognized Microsoft because the signer. Together, these items outlined how a lot I may belief the method.
That means, I used to be checking whether or not the trail, signer, and VirusTotal consequence all informed the identical story.
I nonetheless do not acknowledge most of what is operating
By the time I closed Process Explorer, I nonetheless did not know what half the processes truly do day after day on my PC, however I’m comfortable with it
|
What catches my consideration |
What I test subsequent |
|---|---|
|
A course of I do not acknowledge |
Where its file truly lives |
|
Where its file truly lives |
Who signed it |
|
Still does not add up |
What VirusTotal already is aware of about it |
|
Several indicators pointing the identical means |
Worth investigating correctly |
svchost.exe made the case for me higher than RuntimeBroker.exe did. One occasion (PID 1352) used about 20 MB of personal reminiscence. It’s one of the vital acquainted Windows course of names, however that familiarity does not inform me which companies that specific occasion is internet hosting. The course of title alone is not sufficient. Since malware generally makes use of familiar-looking names, it is vital to test the place the executable sits on the gadget and who signed it.
I nonetheless do not acknowledge many processes, and that is stopped being my purpose. If I do not acknowledge one thing, I now have a method to determine whether or not it is price investigating as a substitute of judging it by the title alone.
Process Explorer gives me several ways to investigate those processes with out having to acknowledge each one in every of them first.